Automate list entries with the List API: getLists, listEntries, addEntries, and deleteEntries, with API key authentication and tenant scopes.
The List API lets you programmatically add, update, and remove entries on all lists that are visible in the web interface, including custom lists. The following endpoints are supported:
getLists
listEntries
addEntries
deleteEntries
For playbook patterns that use these endpoints — and for getting xorlab events into your SOAR in the first place — see Automate with a SOAR.
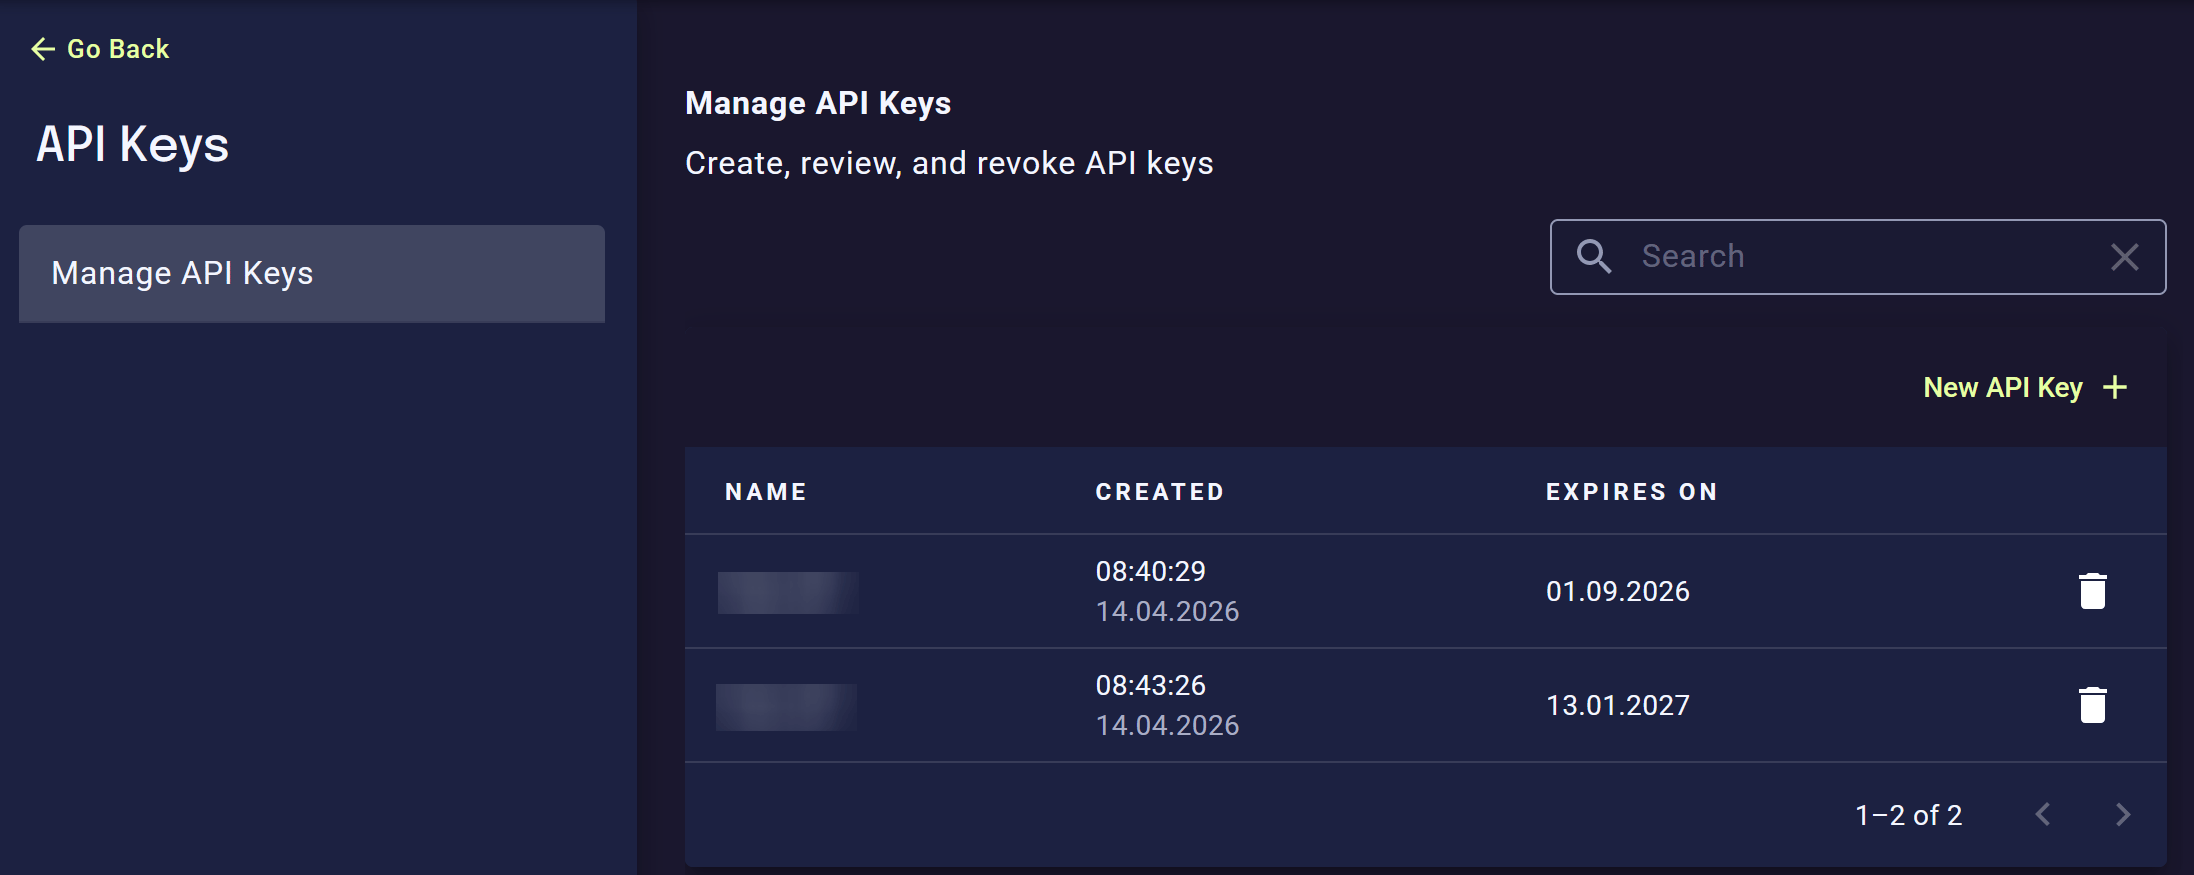
Go to the Admin view in xorlab, and open the API keys configuration.
Create a new API key and store it in a secure location. The key comes with a fixed permission set that only allows manipulating list entries, and nothing else.
Now you can use the key to change lists via the API. Below are some examples.
Get lists
Read all entries
Add
Delete
Use this first to discover which lists are available. For the global scope, set tenantUid to null:
Base URL of your xorlab instance, for example https://xyz.activeguard.cloud.
<api-key>
API key created in the XCC web interface.
<tenant-uid>
Use null for the global scope. If you want to access a tenant-scoped list, set it to the uid parameter of that tenant as found in the guarded_tenants.yml.
<list-name>
Internal list name, for example BLACKLIST_local_sender_addresses.
Each list has a maximum size. The exact limit depends on the list type and is returned by the getLists endpoint as maxSize.The most important behavior to understand is what happens when a list is already full:
Automatic cleanup of full listsIf a list has reached its maximum size and you add a new entry, xorlab automatically removes the oldest existing entry from that list.
This means:
New entries can still always be added
The list size never grows beyond its configured maximum
Older entries may disappear automatically if the list is already full
If needed, you can still manage list entries manually either through the Lists page or through configuration files in the Expert Editor. However the same automatic cleanup applies.
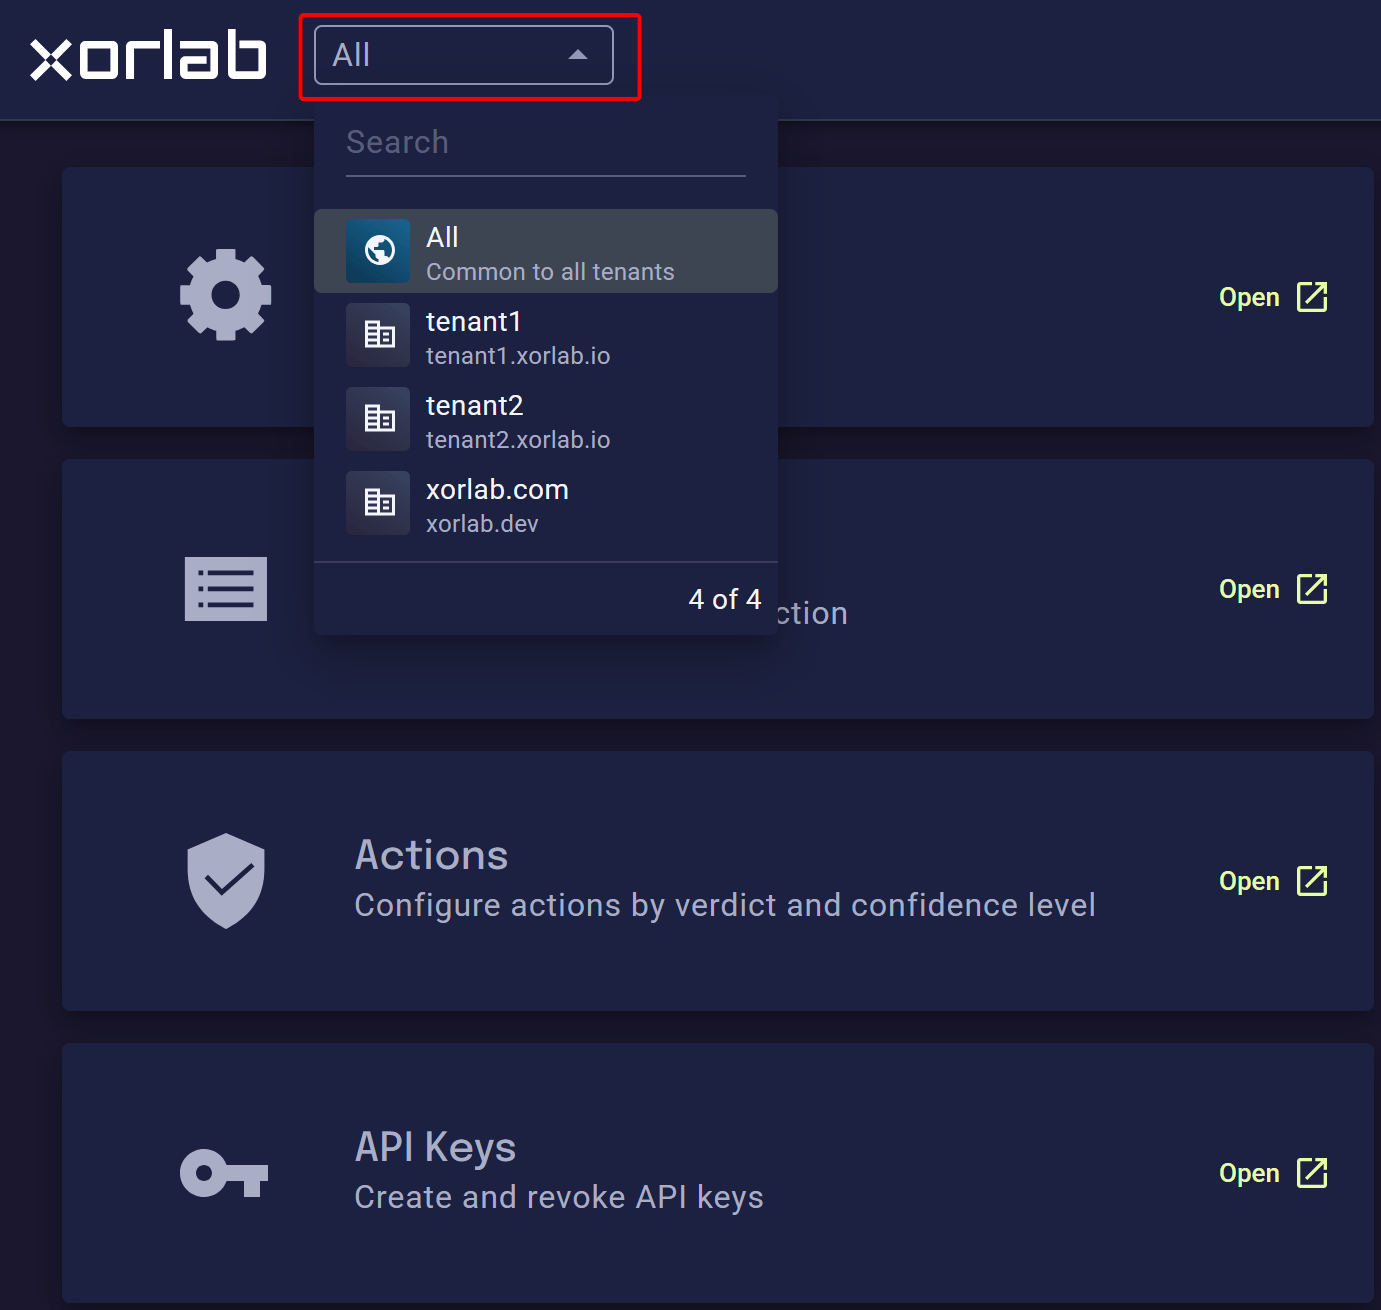
The scope where a key is created determines what it can access.
A tenant-scoped key can manipulate list entries only within that tenant
A globally scoped key can manipulate list entries for all tenants and for the global scope of the instance
The scope cannot be changed afterward, so create a separate key per automation with the narrowest scope that works. Together with the fixed permission set, this keeps the impact of a leaked key limited to the list entries of one tenant.
Each endpoint has its own reference page in the sidebar below this one, generated
from the OpenAPI specification: request and response schemas, error codes, and a
playground you can call your own instance from.The specification itself is on List API OpenAPI Spec, in one
block you can copy into your API tooling or hand to a client generator.
Assistant
Responses are generated using AI and may contain mistakes.