

Choose how to configure it
Both paths create the same two connectors and the same two mail flow rules. Pick one.Quick integration with PowerShell
Run one script that asks for your values. Mail flow rules need to be activated manually.
Manual integration in the Exchange Admin Center
The same configuration manually in the web interface. Use it if you prefer to see each setting before you apply it.
Quick integration with PowerShell
One script creates both connectors and both mail flow rules. It asks for your values, shows a summary and changes nothing until you confirm. You need the Exchange Administrator role and theExchangeOnlineManagement module. Run it either in a PowerShell window on your own machine or in the Azure Cloud Shell.
Installing ExchangeOnlineManagement module locally
Installing ExchangeOnlineManagement module locally
Run these once, in a PowerShell window on your own machine. Everything installs for your user account only, so you do not need local administrator rights:
-
Download the script with the command on Script Downloads, which requires you to log in. Run that command in your PowerShell window, then come back here and start the script. If you are not signed in to Exchange Online yet, a sign-in window opens first:
If one of the connectors or rules already exists in your tenant, the script stops without changing anything.
-
Answer the prompts:
-
Check the summary and confirm with
y. The script then:- creates the
xorlabToMicrosoft365andMicrosoft365Toxorlabconnectors - validates
Microsoft365Toxorlaband summarizes the result - creates the
IncomingToxorlabandOutgoingToxorlabmail flow rules, disabled
- creates the
-
Enable both rules:
This is the step that puts xorlab in the delivery path. It can take several minutes until the rules are active. Test them by sending an incoming and an outgoing email.
./xorlabExoSetup.ps1 -Mode Inline -Remove.
Test with one mailbox first
With thetest scope, each rule gets one extra condition on top of its organization-wide ones: IncomingToxorlab matches only email to the test mailbox, and OutgoingToxorlab only email from it. All other email keeps its normal mail flow.
When you are done testing, remove that condition and the same rules apply to the whole organization. Either delete it in the Exchange Admin Center under Mail flow → Rules — The recipient → is this person on the incoming rule, The sender → is this person on the outgoing one — or run:
Manual integration in the Exchange Admin Center
Create xorlab to M365 connector
This connector makes sure that M365 will accept emails from xorlab.-
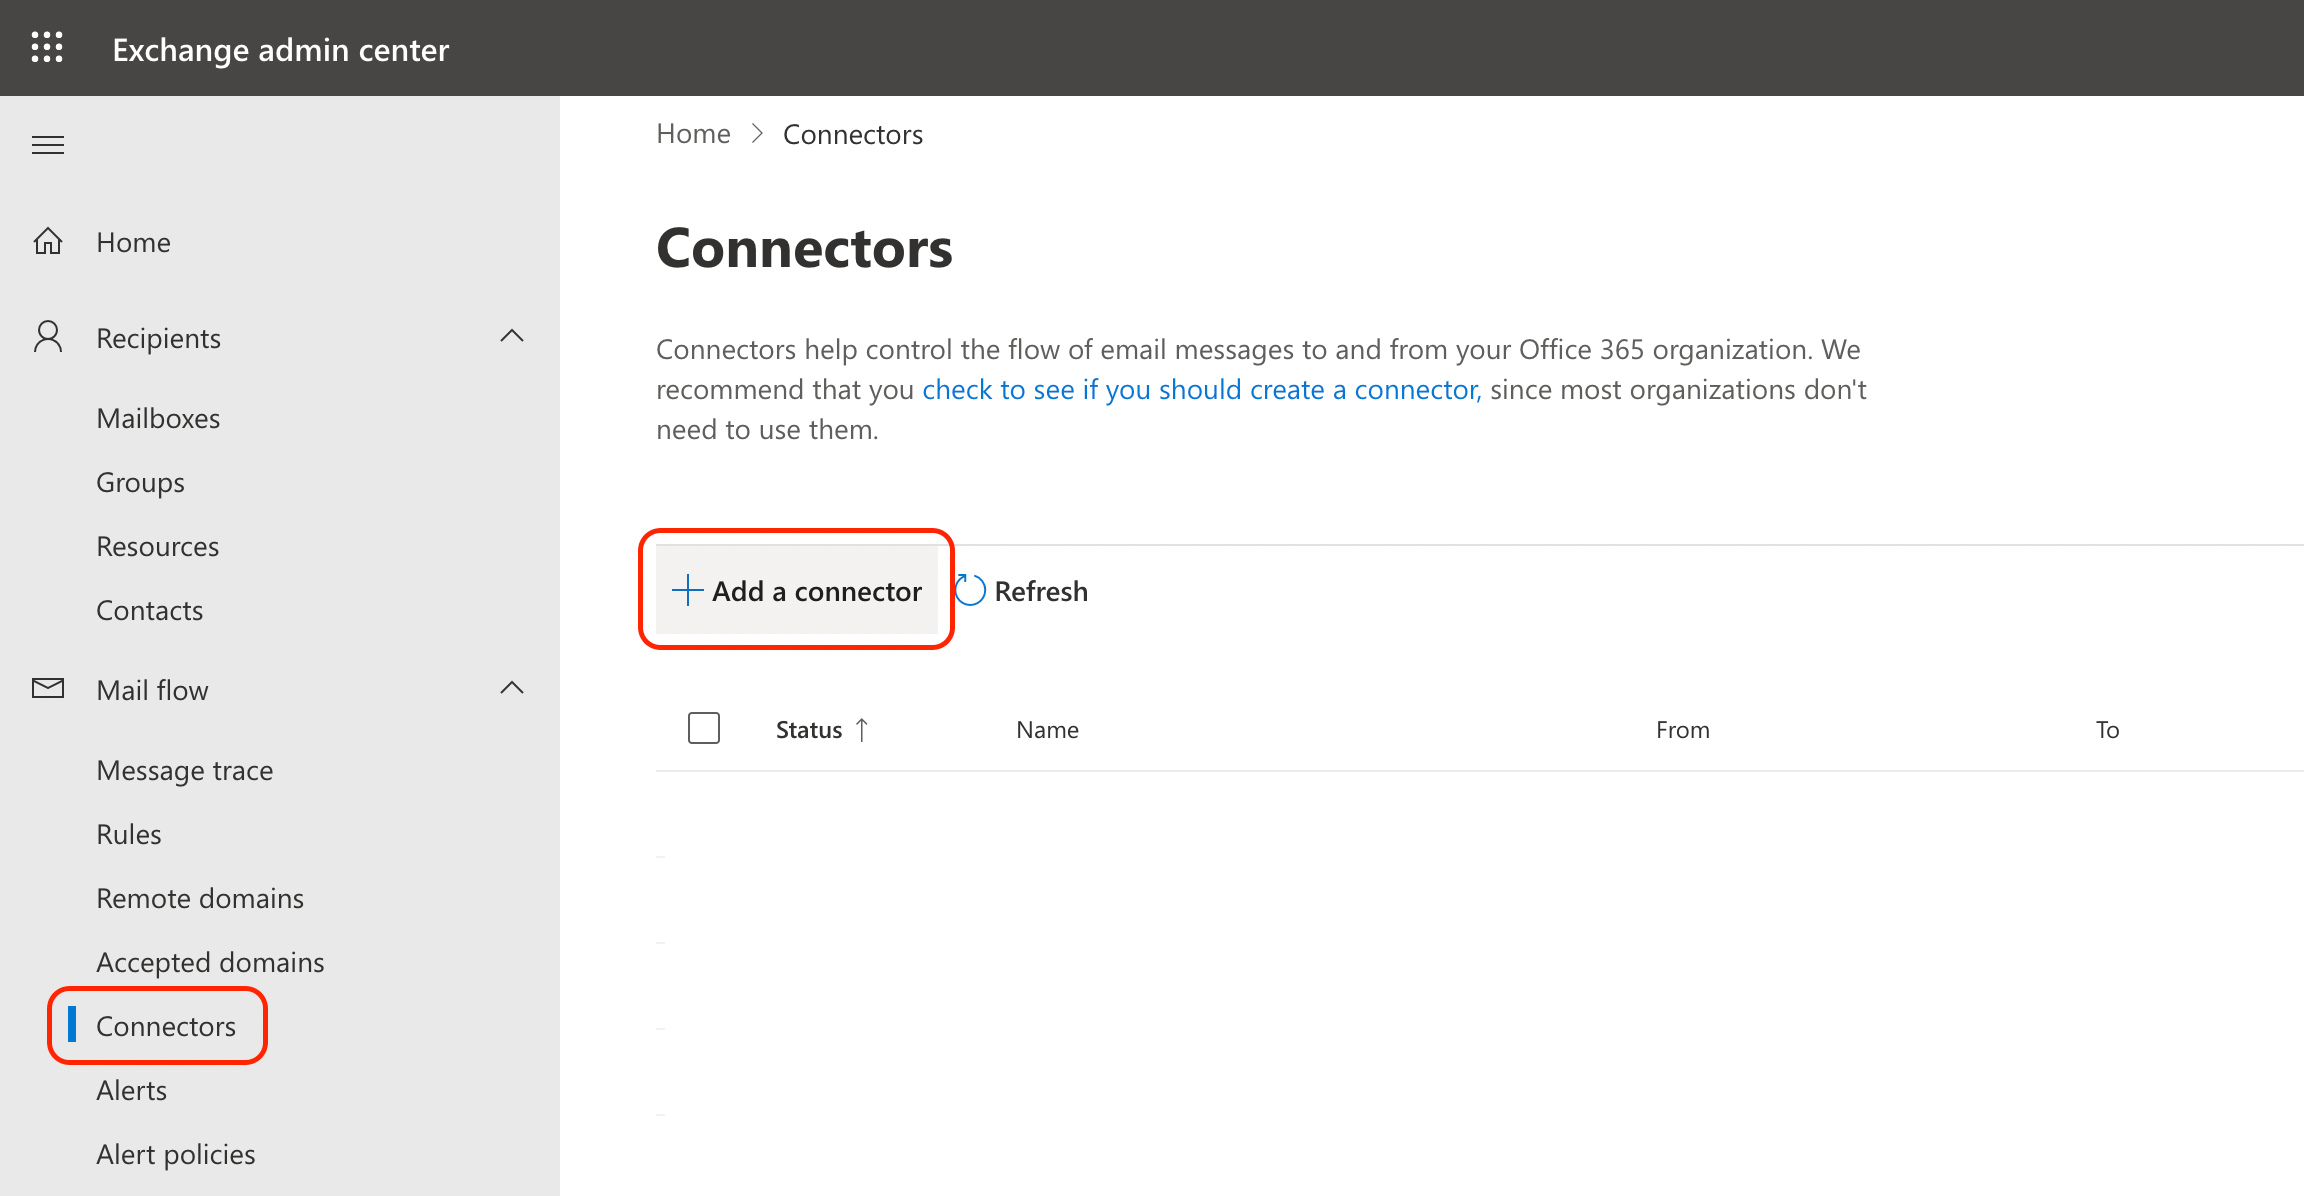
Go to Exchange Admin Center → Connectors → add a connector:
-
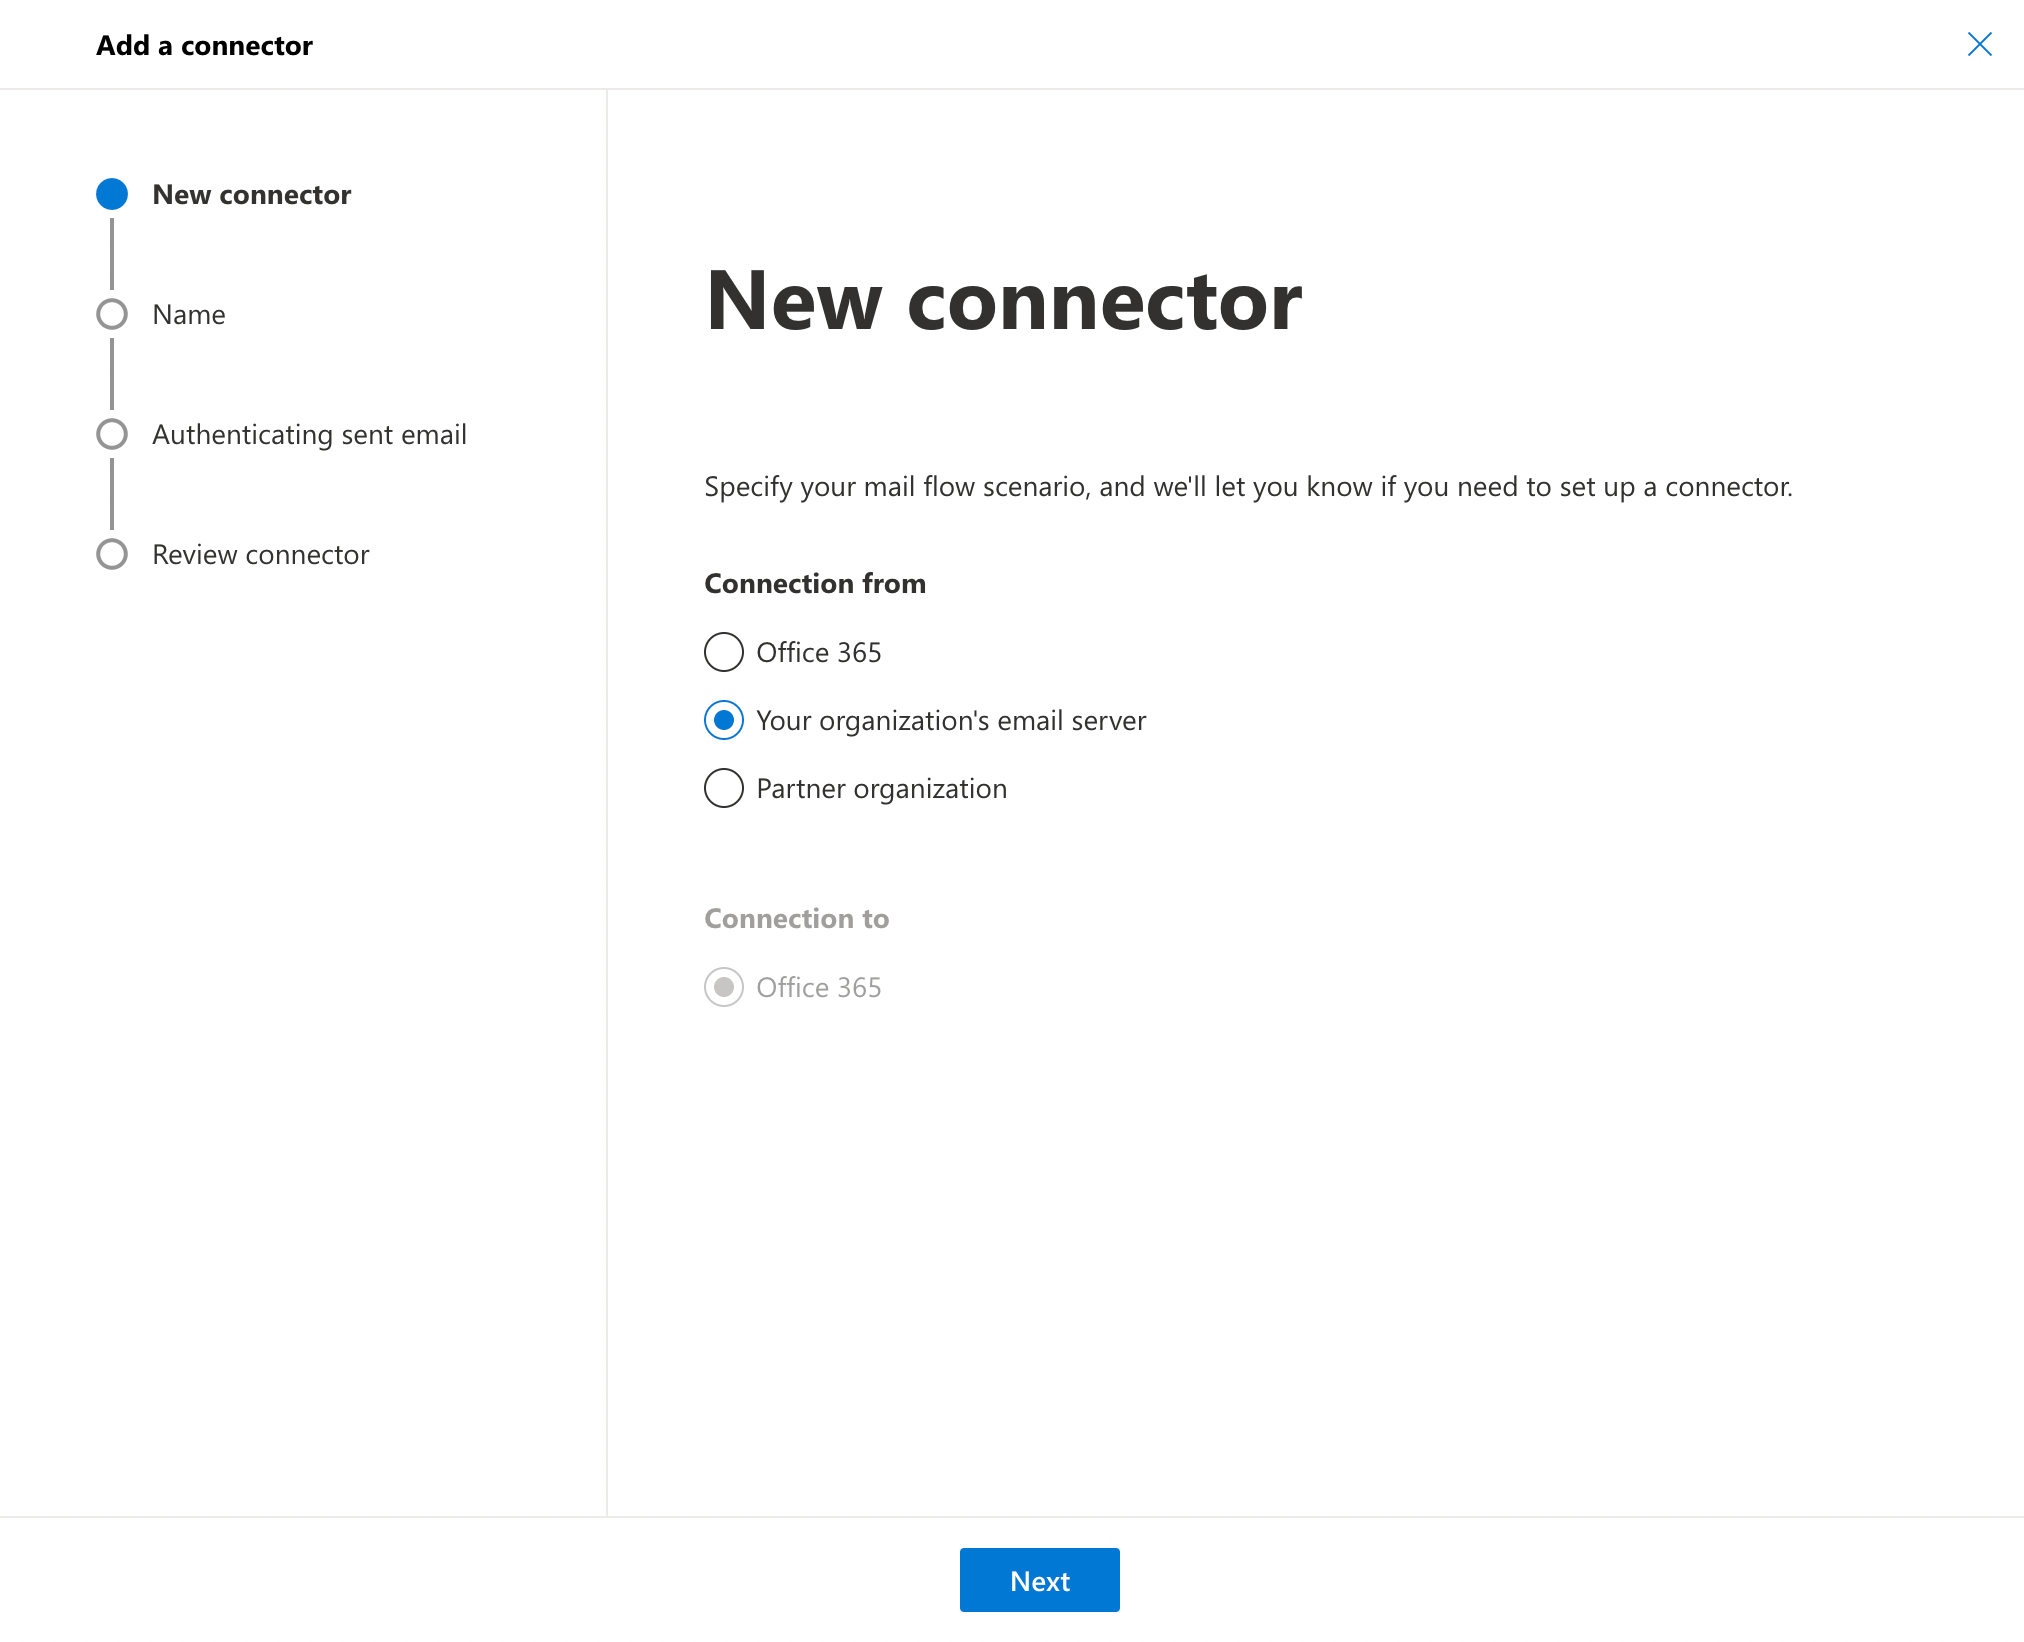
Connection from → Your organization’s email server:
-
Set the name to
xorlabToMicrosoft365and enable Retain internal Exchange email headers: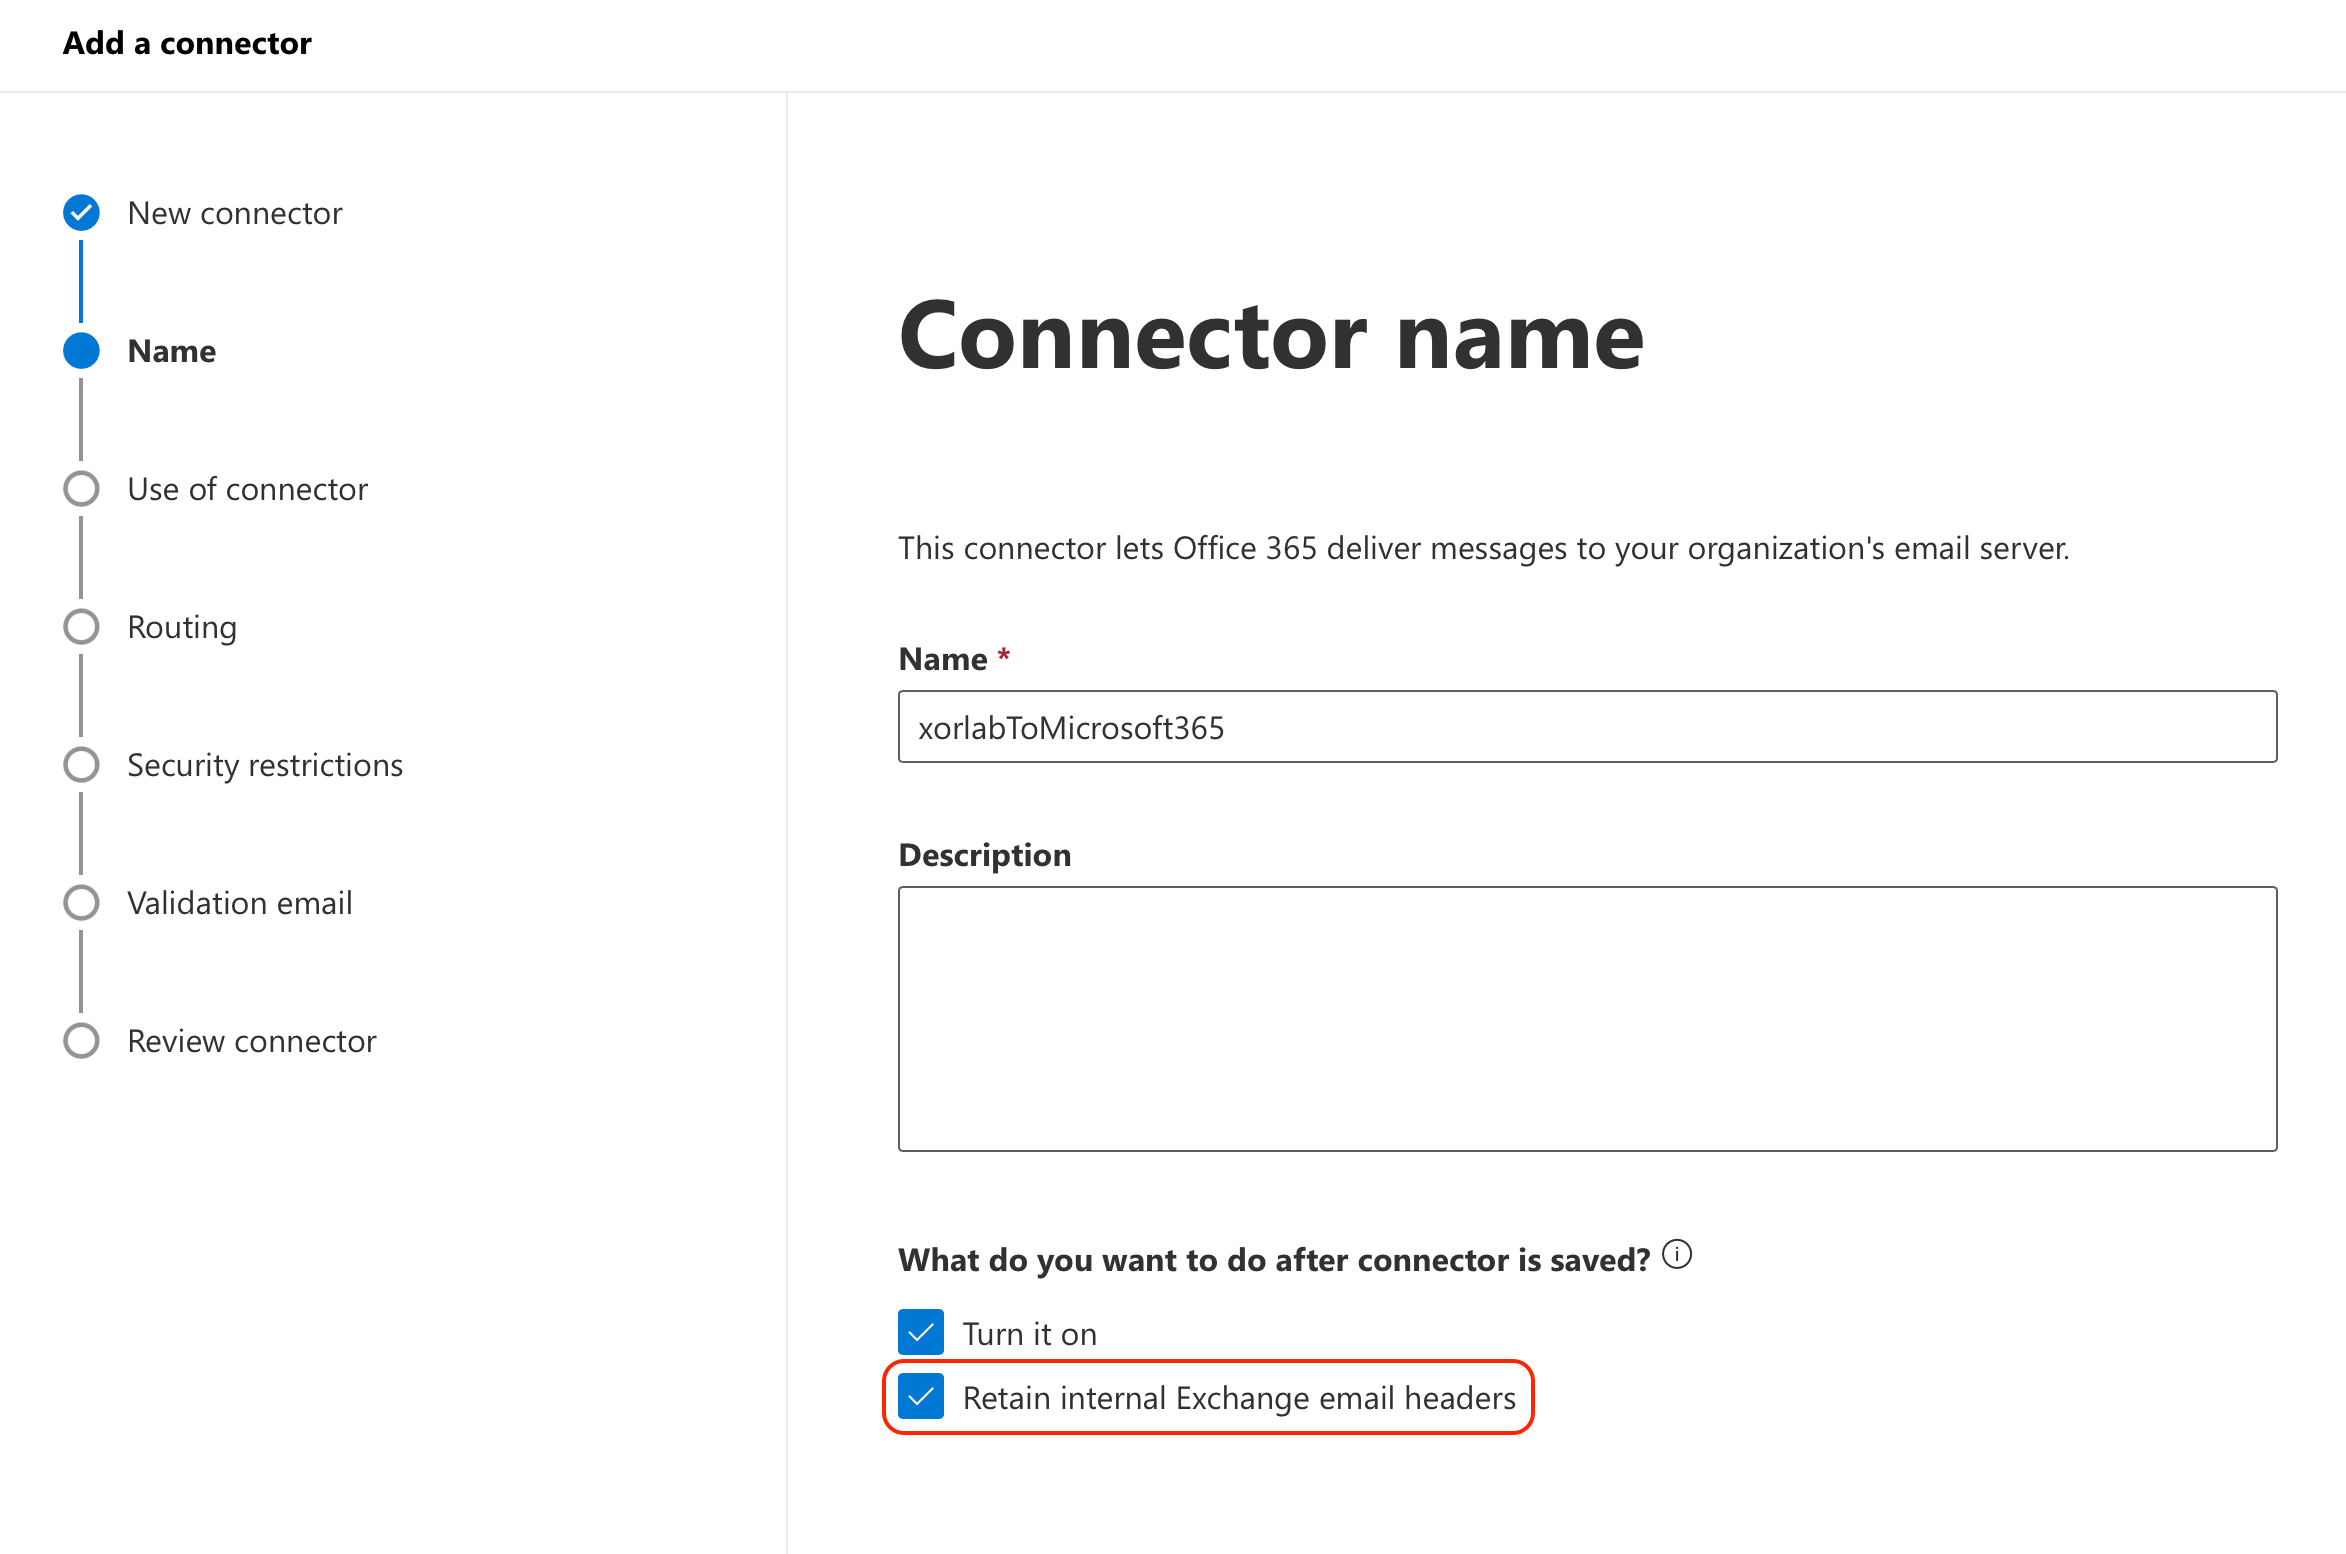
-
Choose By verifying that the subject name… and add
*.xyz.activeguard.cloudwherexyzis your customer ID: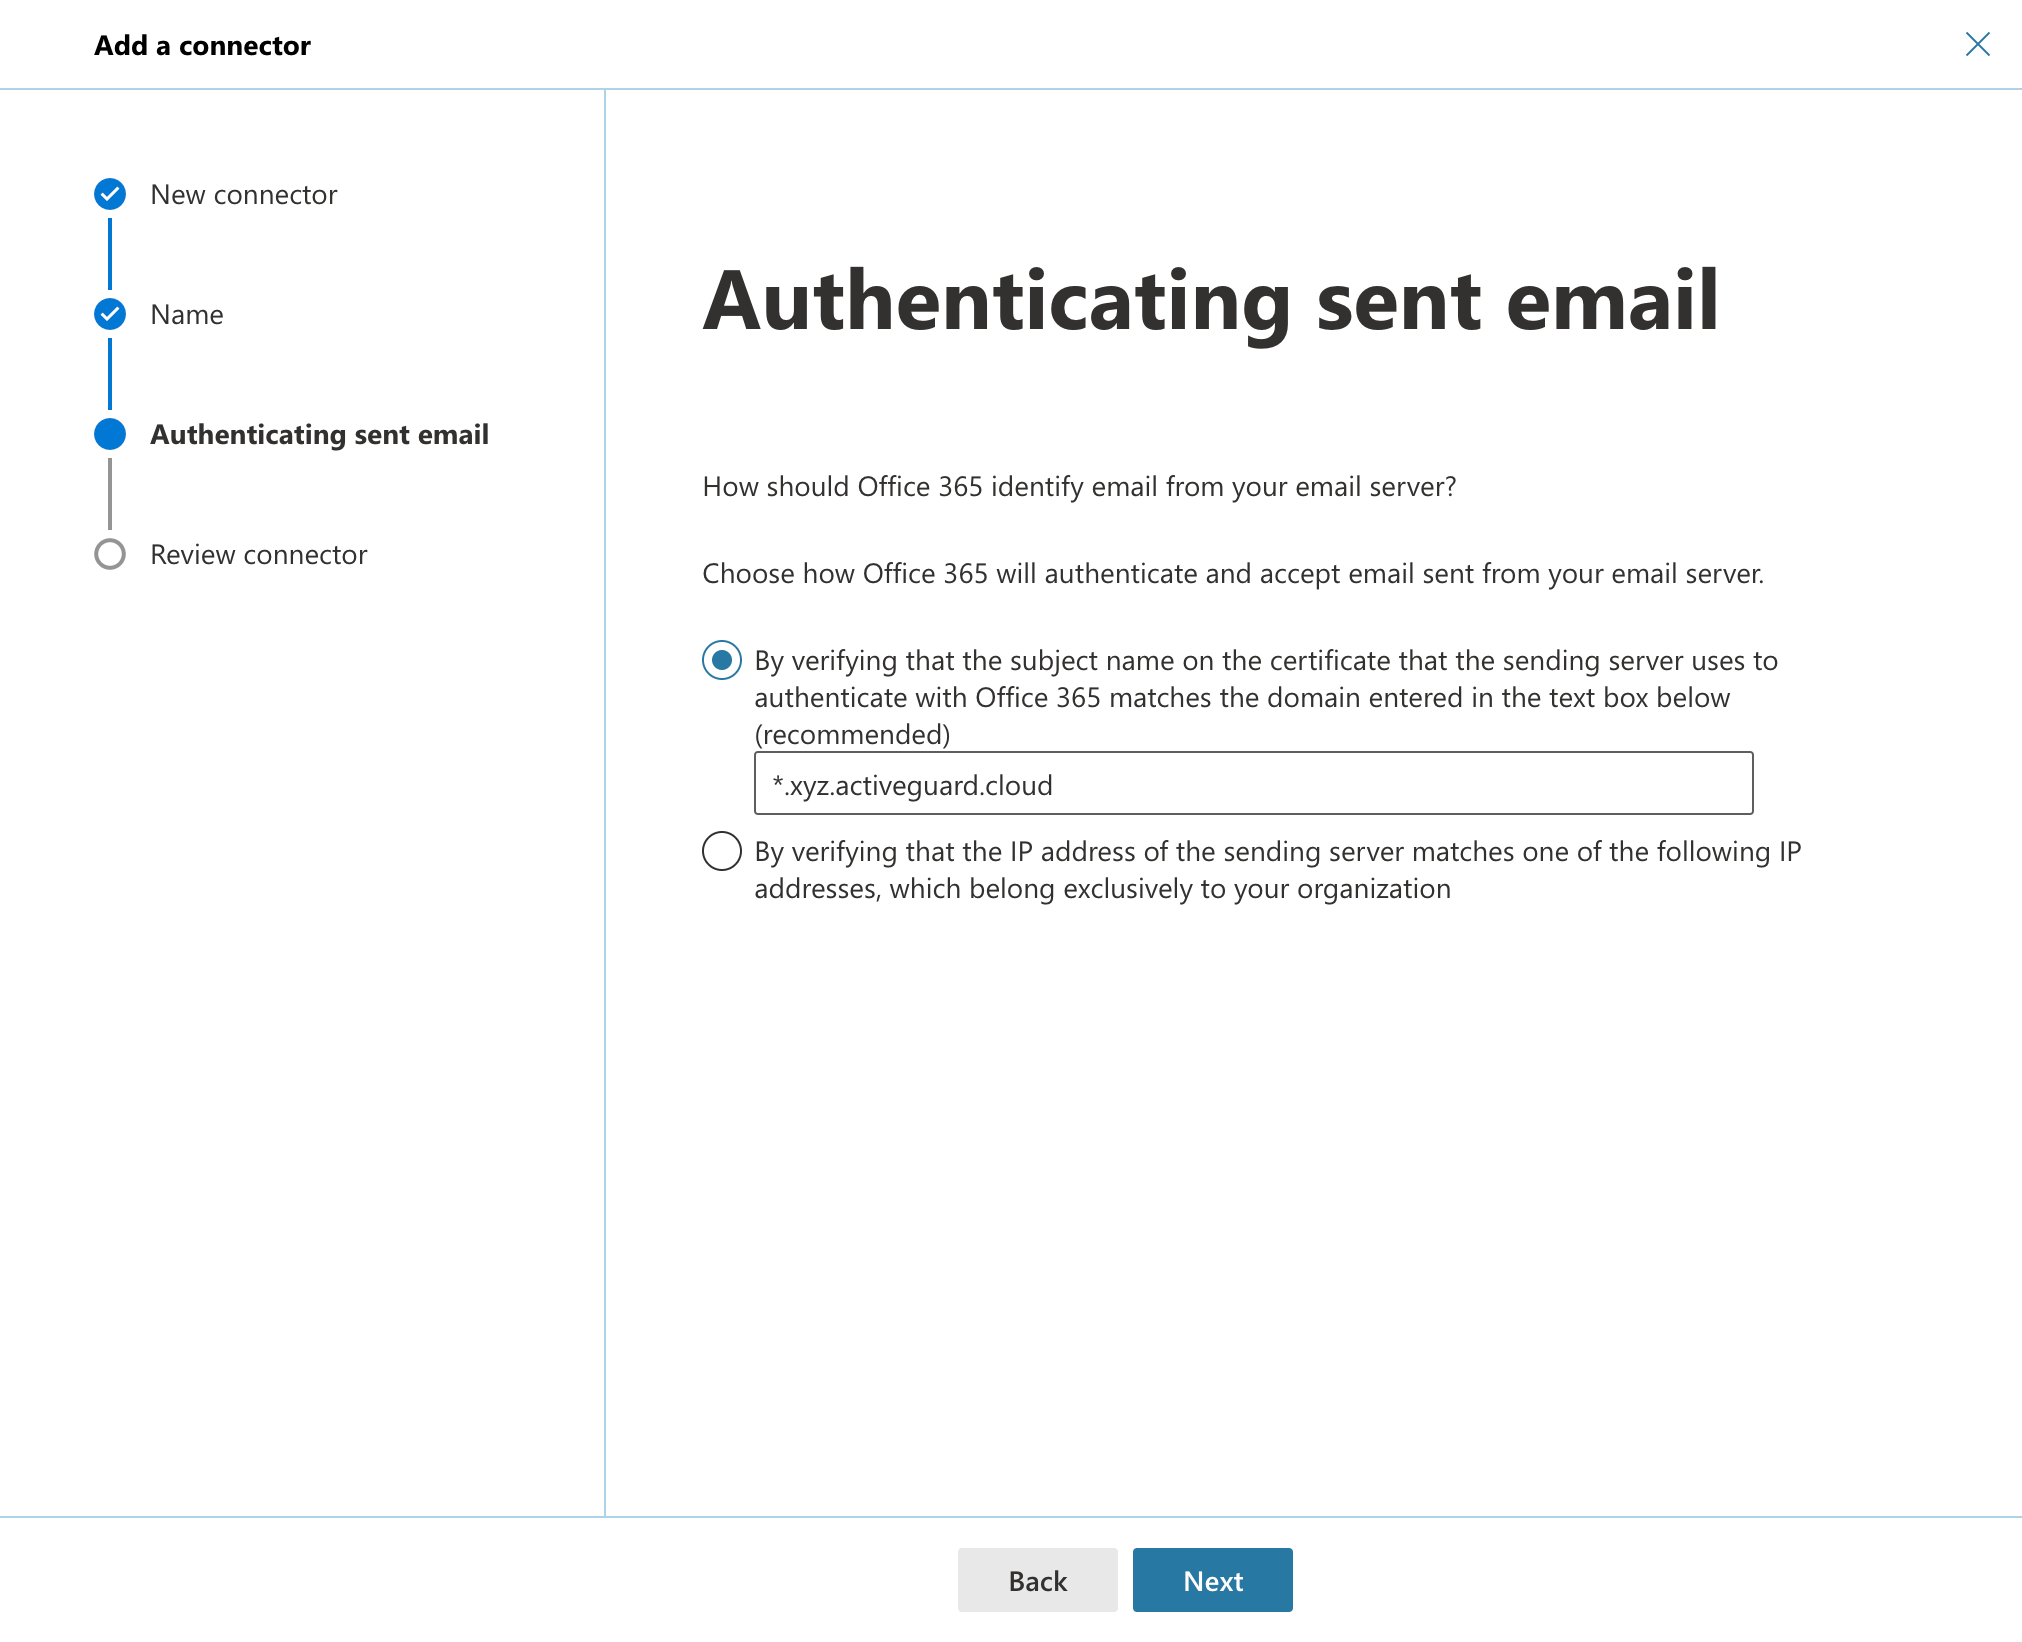
- Create connector.
Create M365 to xorlab connector
This connector makes sure that all emails are routed through xorlab.- Create a new connector.
-
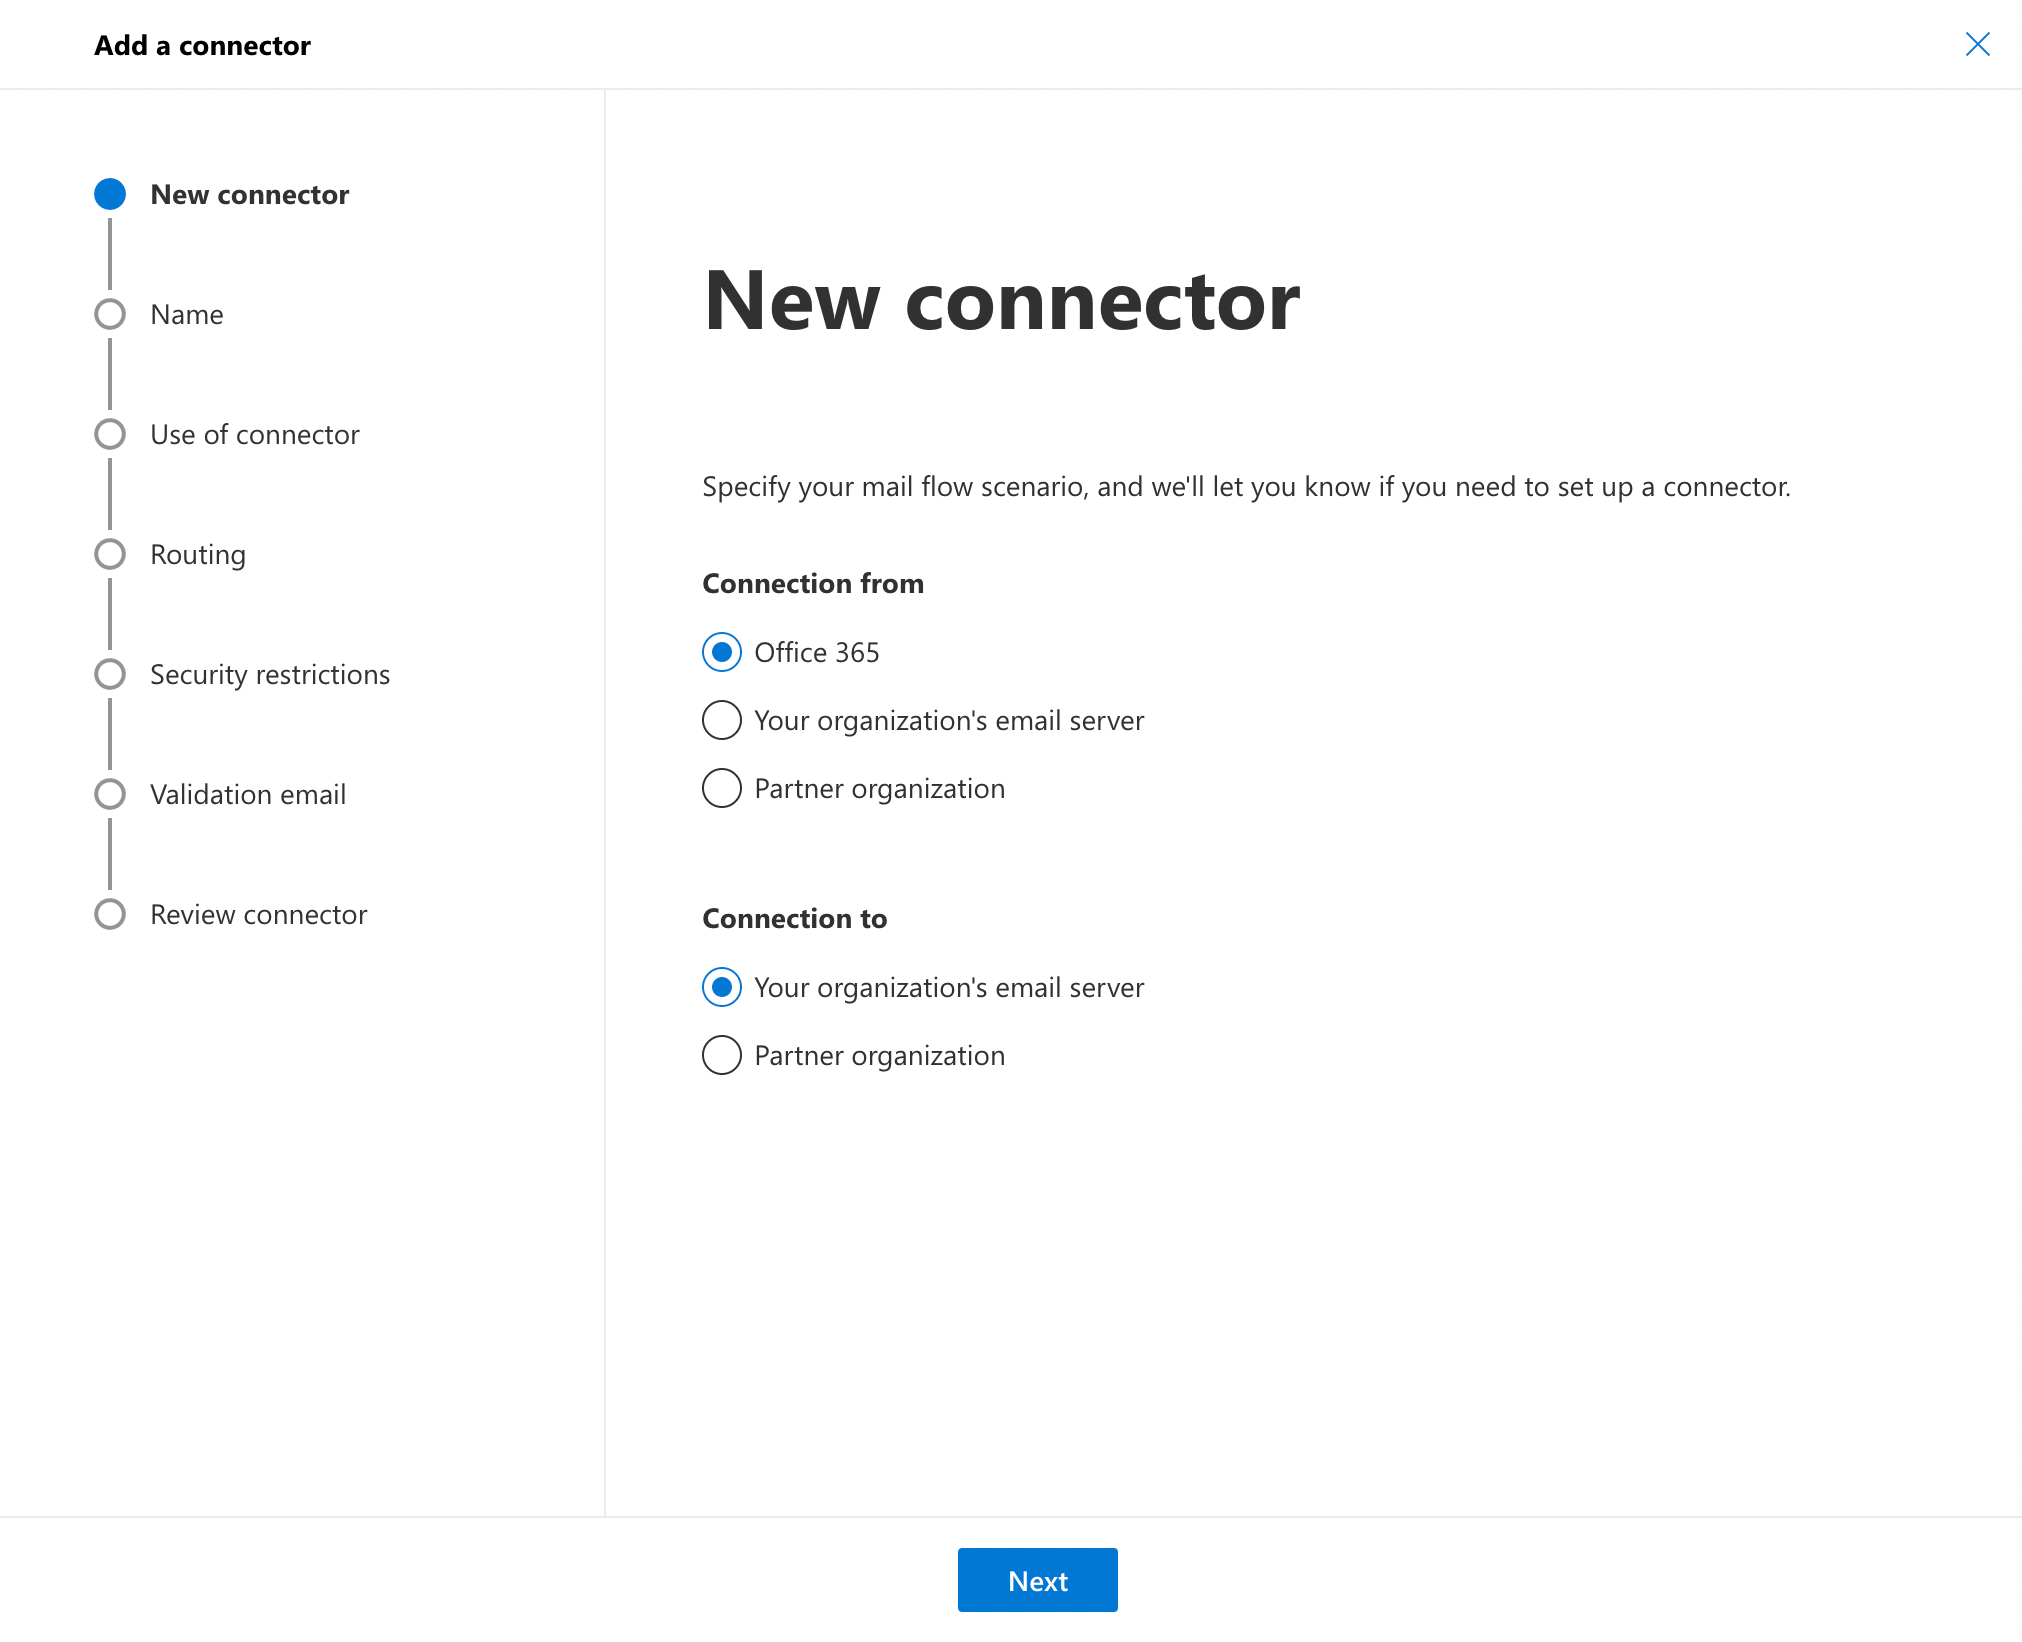
Connection from → Office 365, and Connection to → Your organization’s email server:
-
Set the name to
Microsoft365Toxorlaband enable Retain internal Exchange email headers: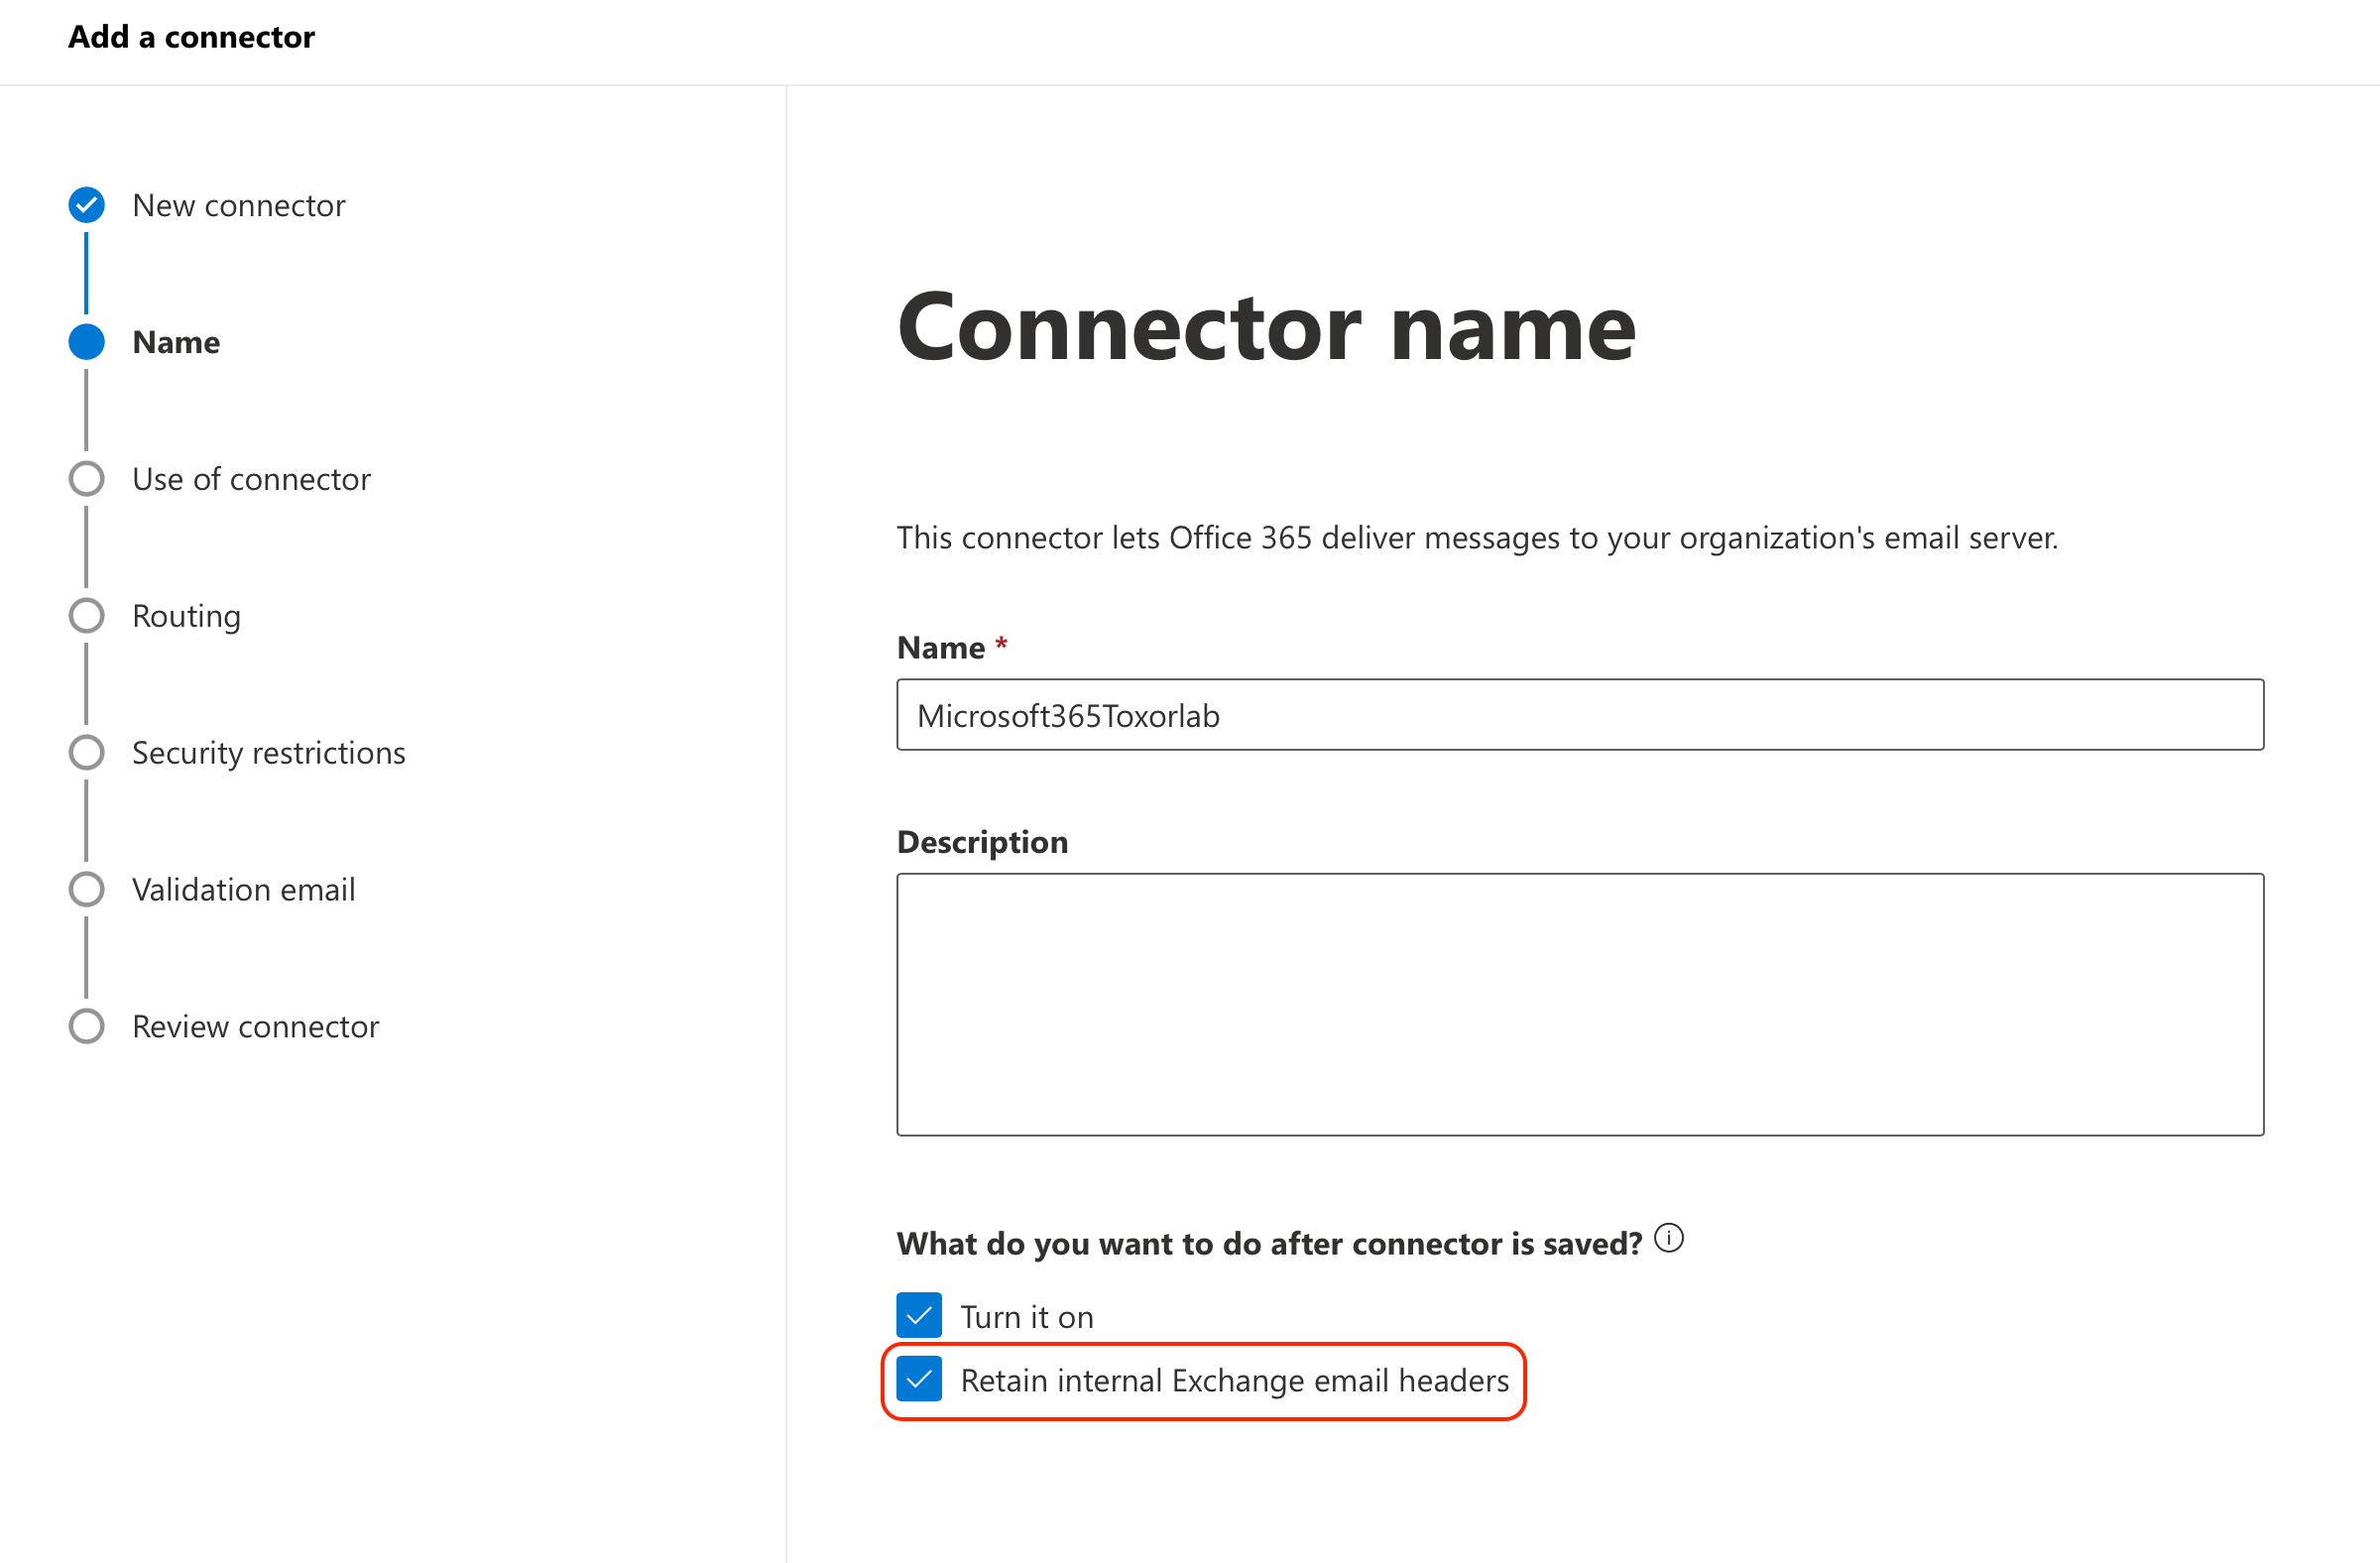
-
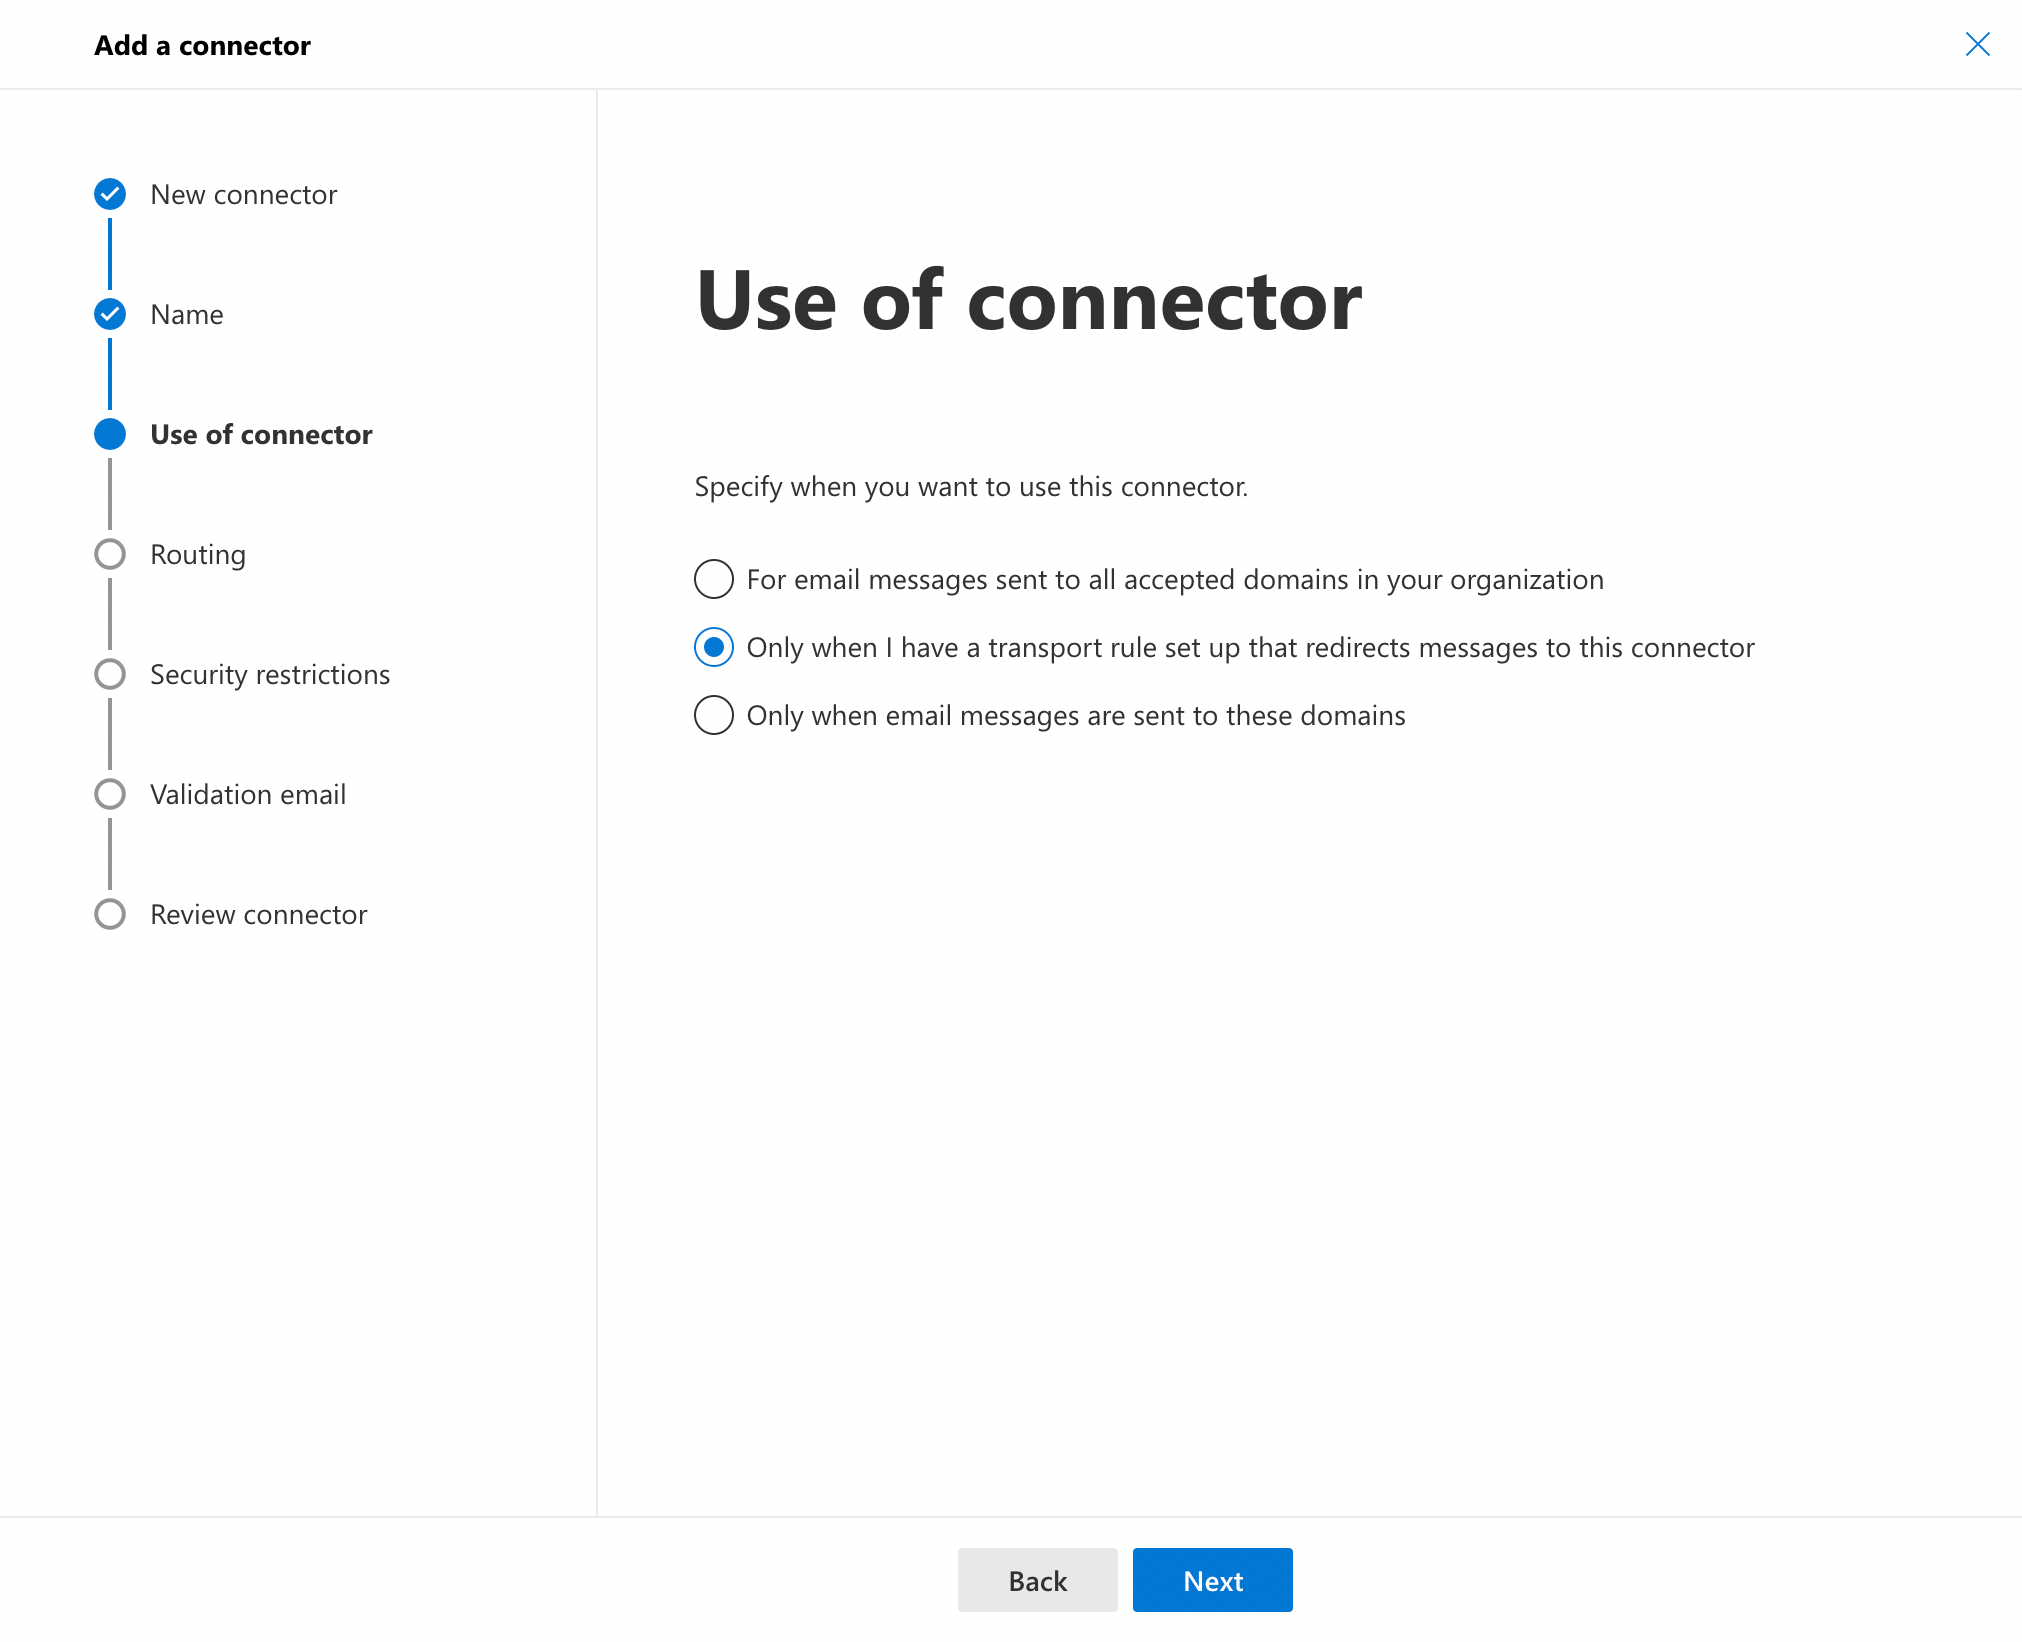
Select Only when I have a transport rule set up…:
-
Add a new smart host with the value
mx.xyz.activeguard.cloud, wherexyzis your customer ID: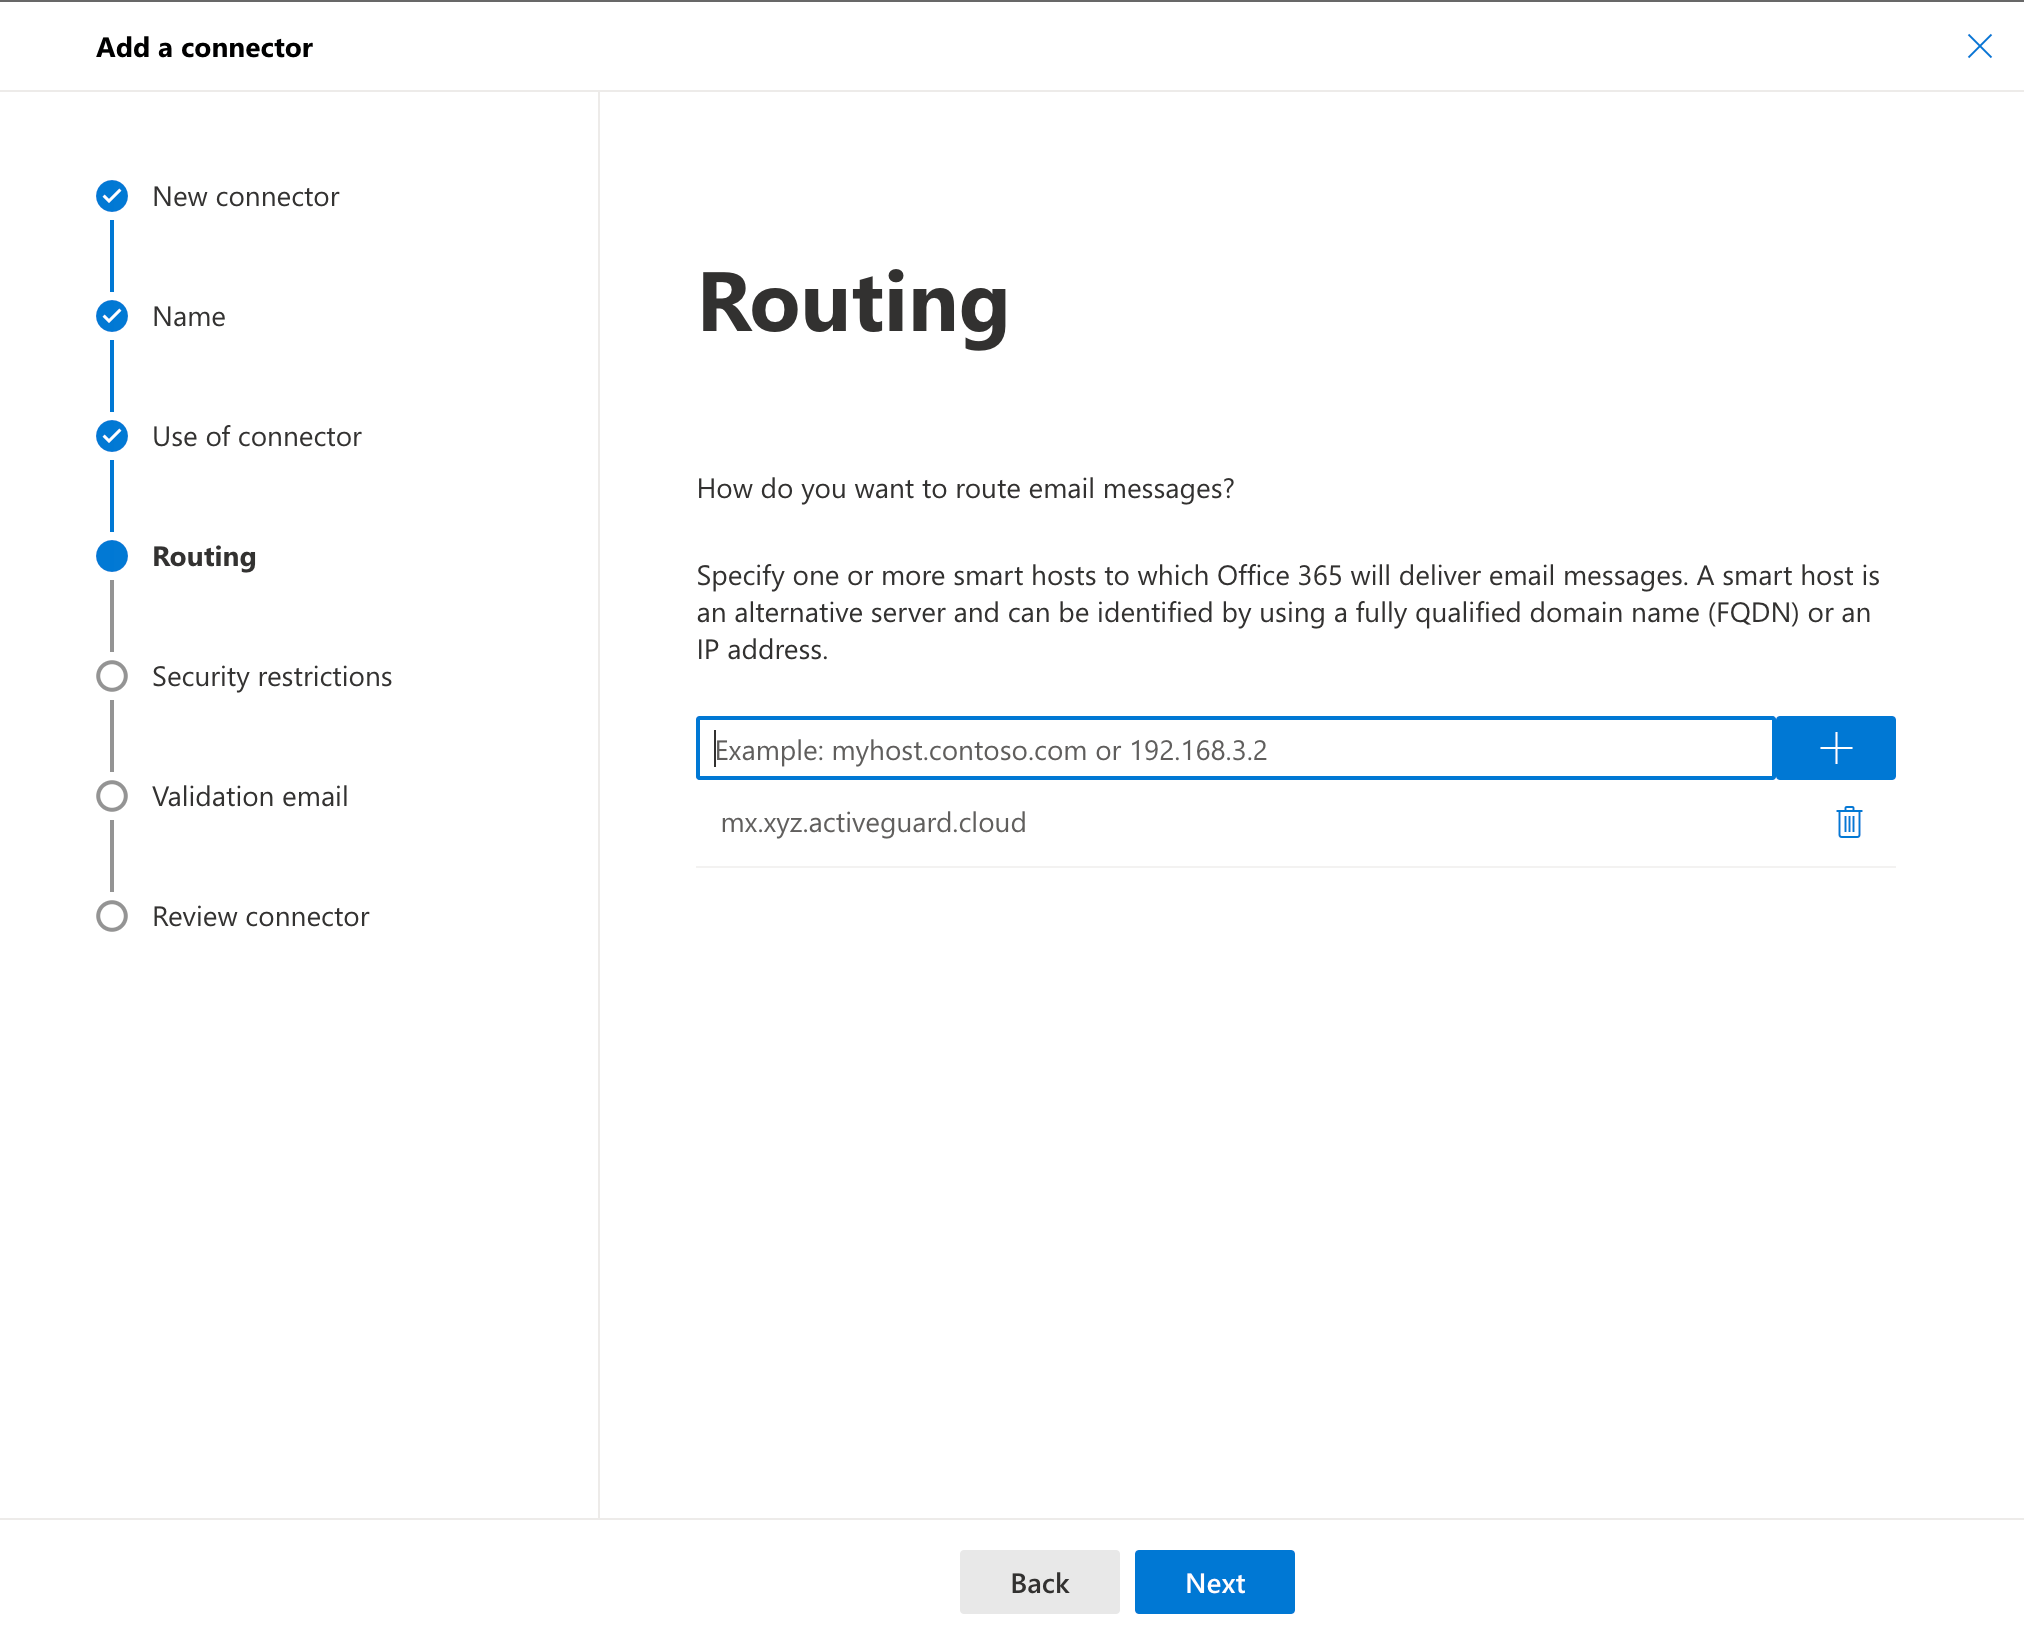
-
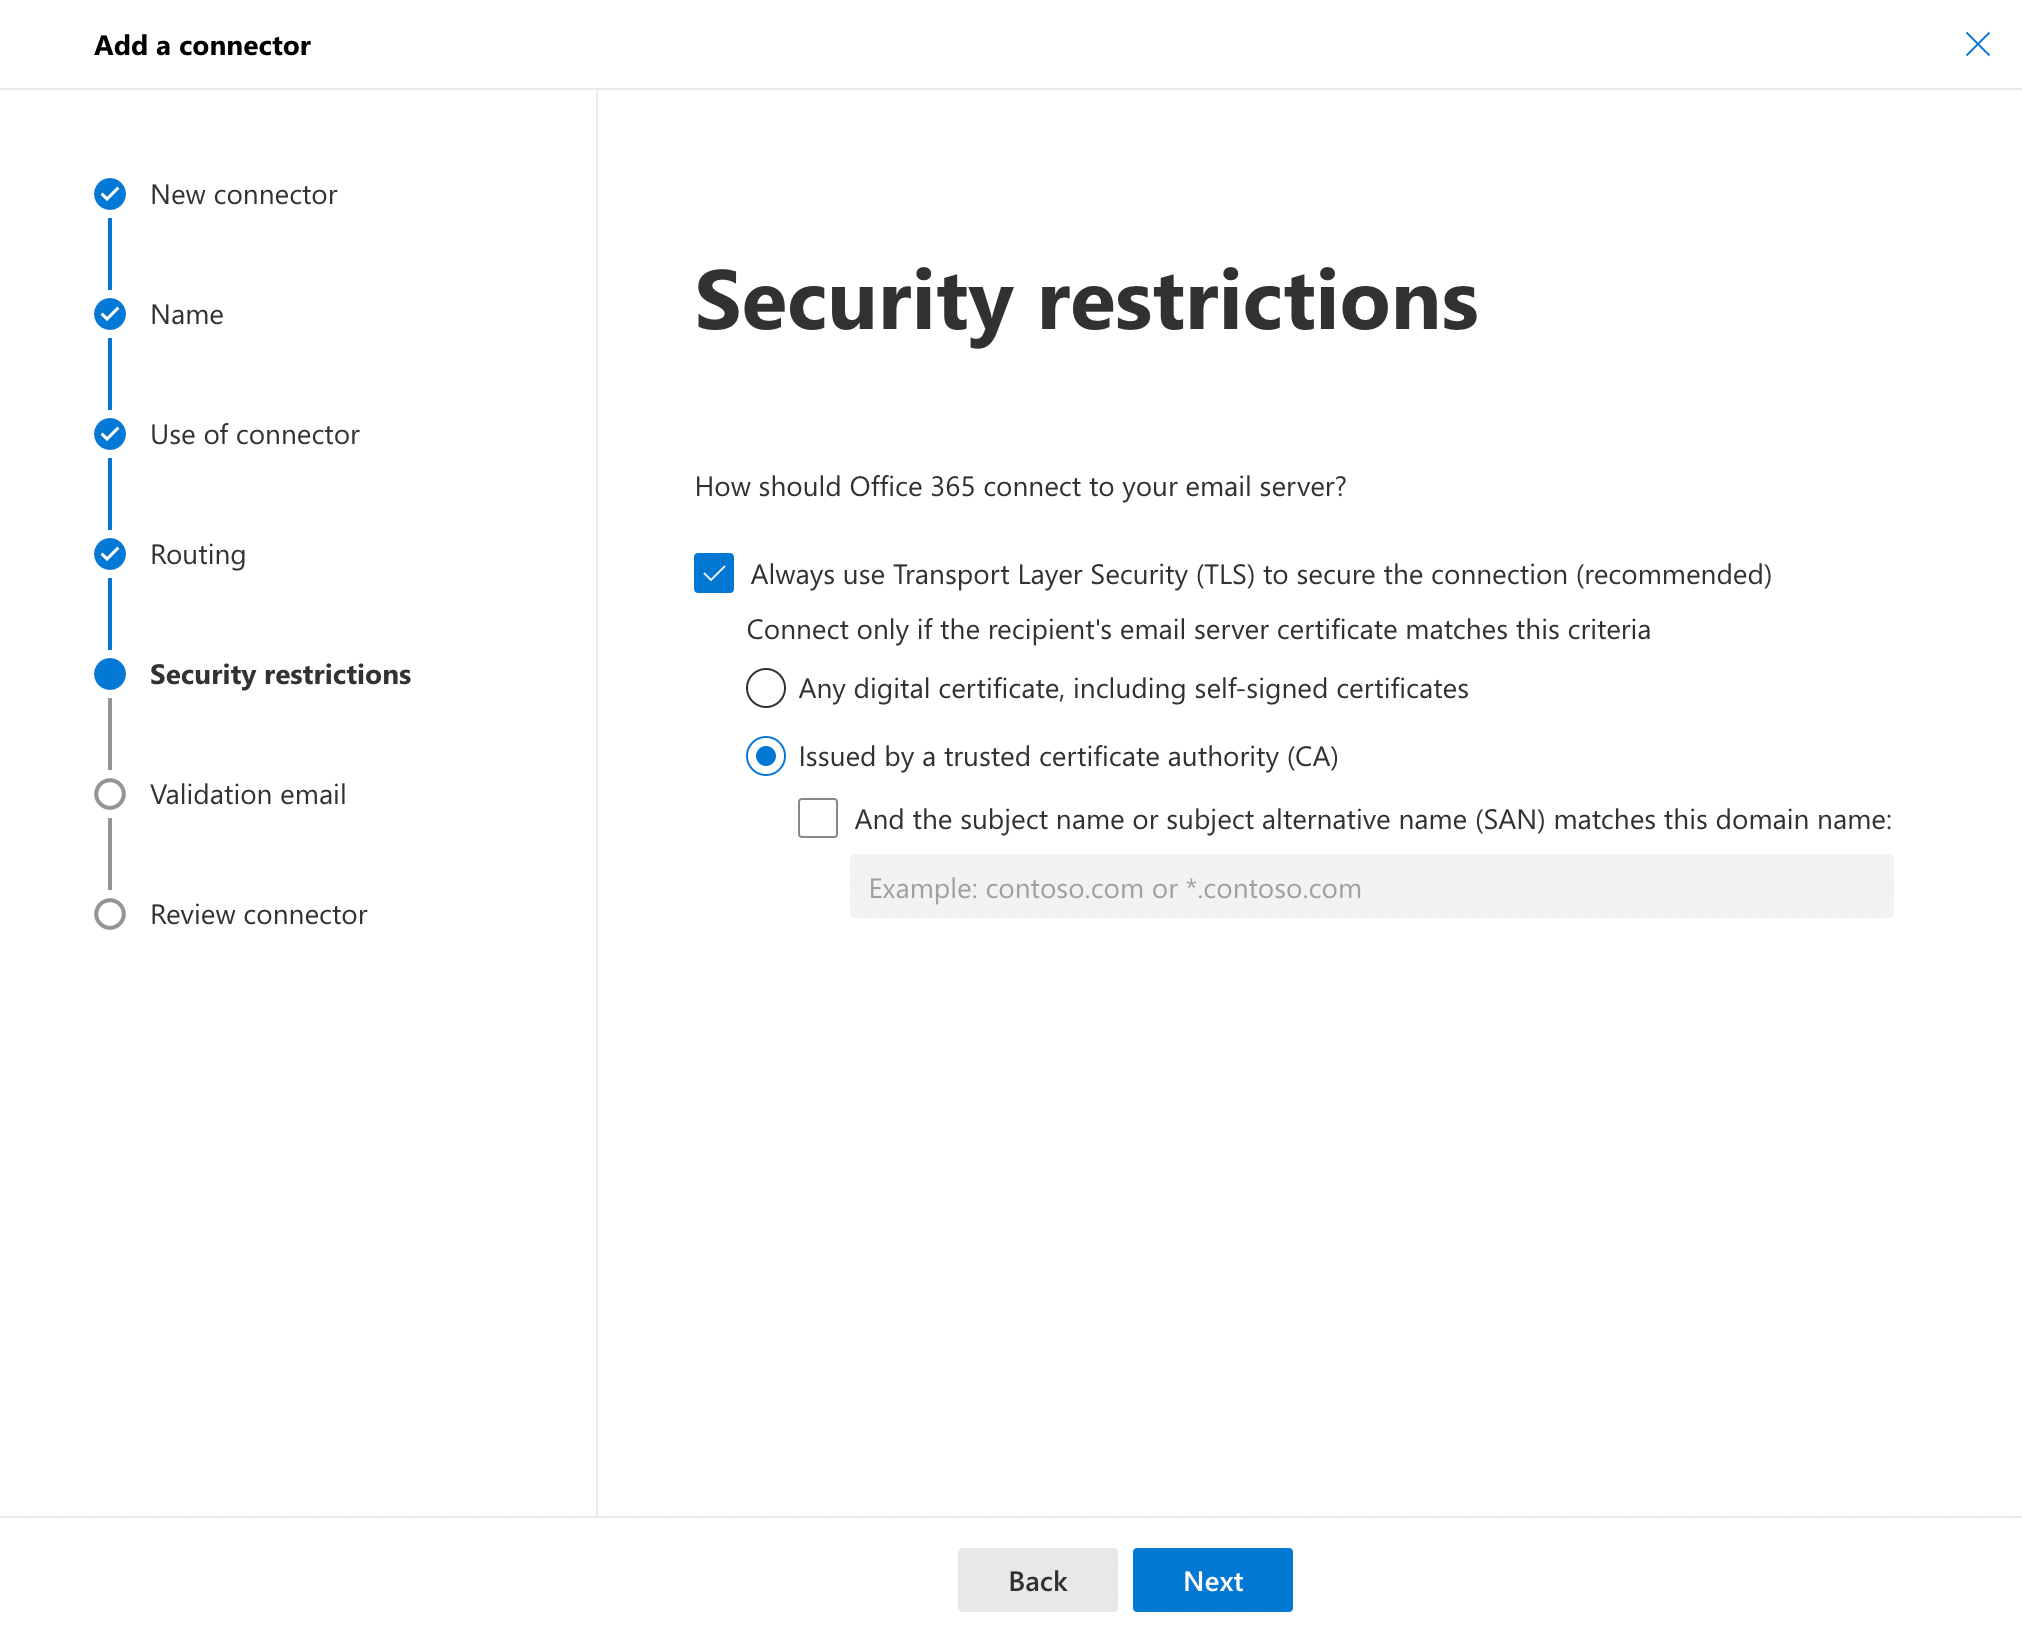
Activate Always use Transport Layer Security… and select Issued by a trusted certificate authority (CA):
-
Enter a company mailbox where a validation email should be sent to:
 Unsuccessful validationThe connector validation might fail at this point. If this happens, save the connector without validation, create the mail flow rule in the next section and then validate the connector again.
- Review the connector and click Create when it’s OK.
Create mail flow rules
Here we create mail flow rules that use the connector from above. The mail flow rules make sure that there is no loop between xorlab and M365.-
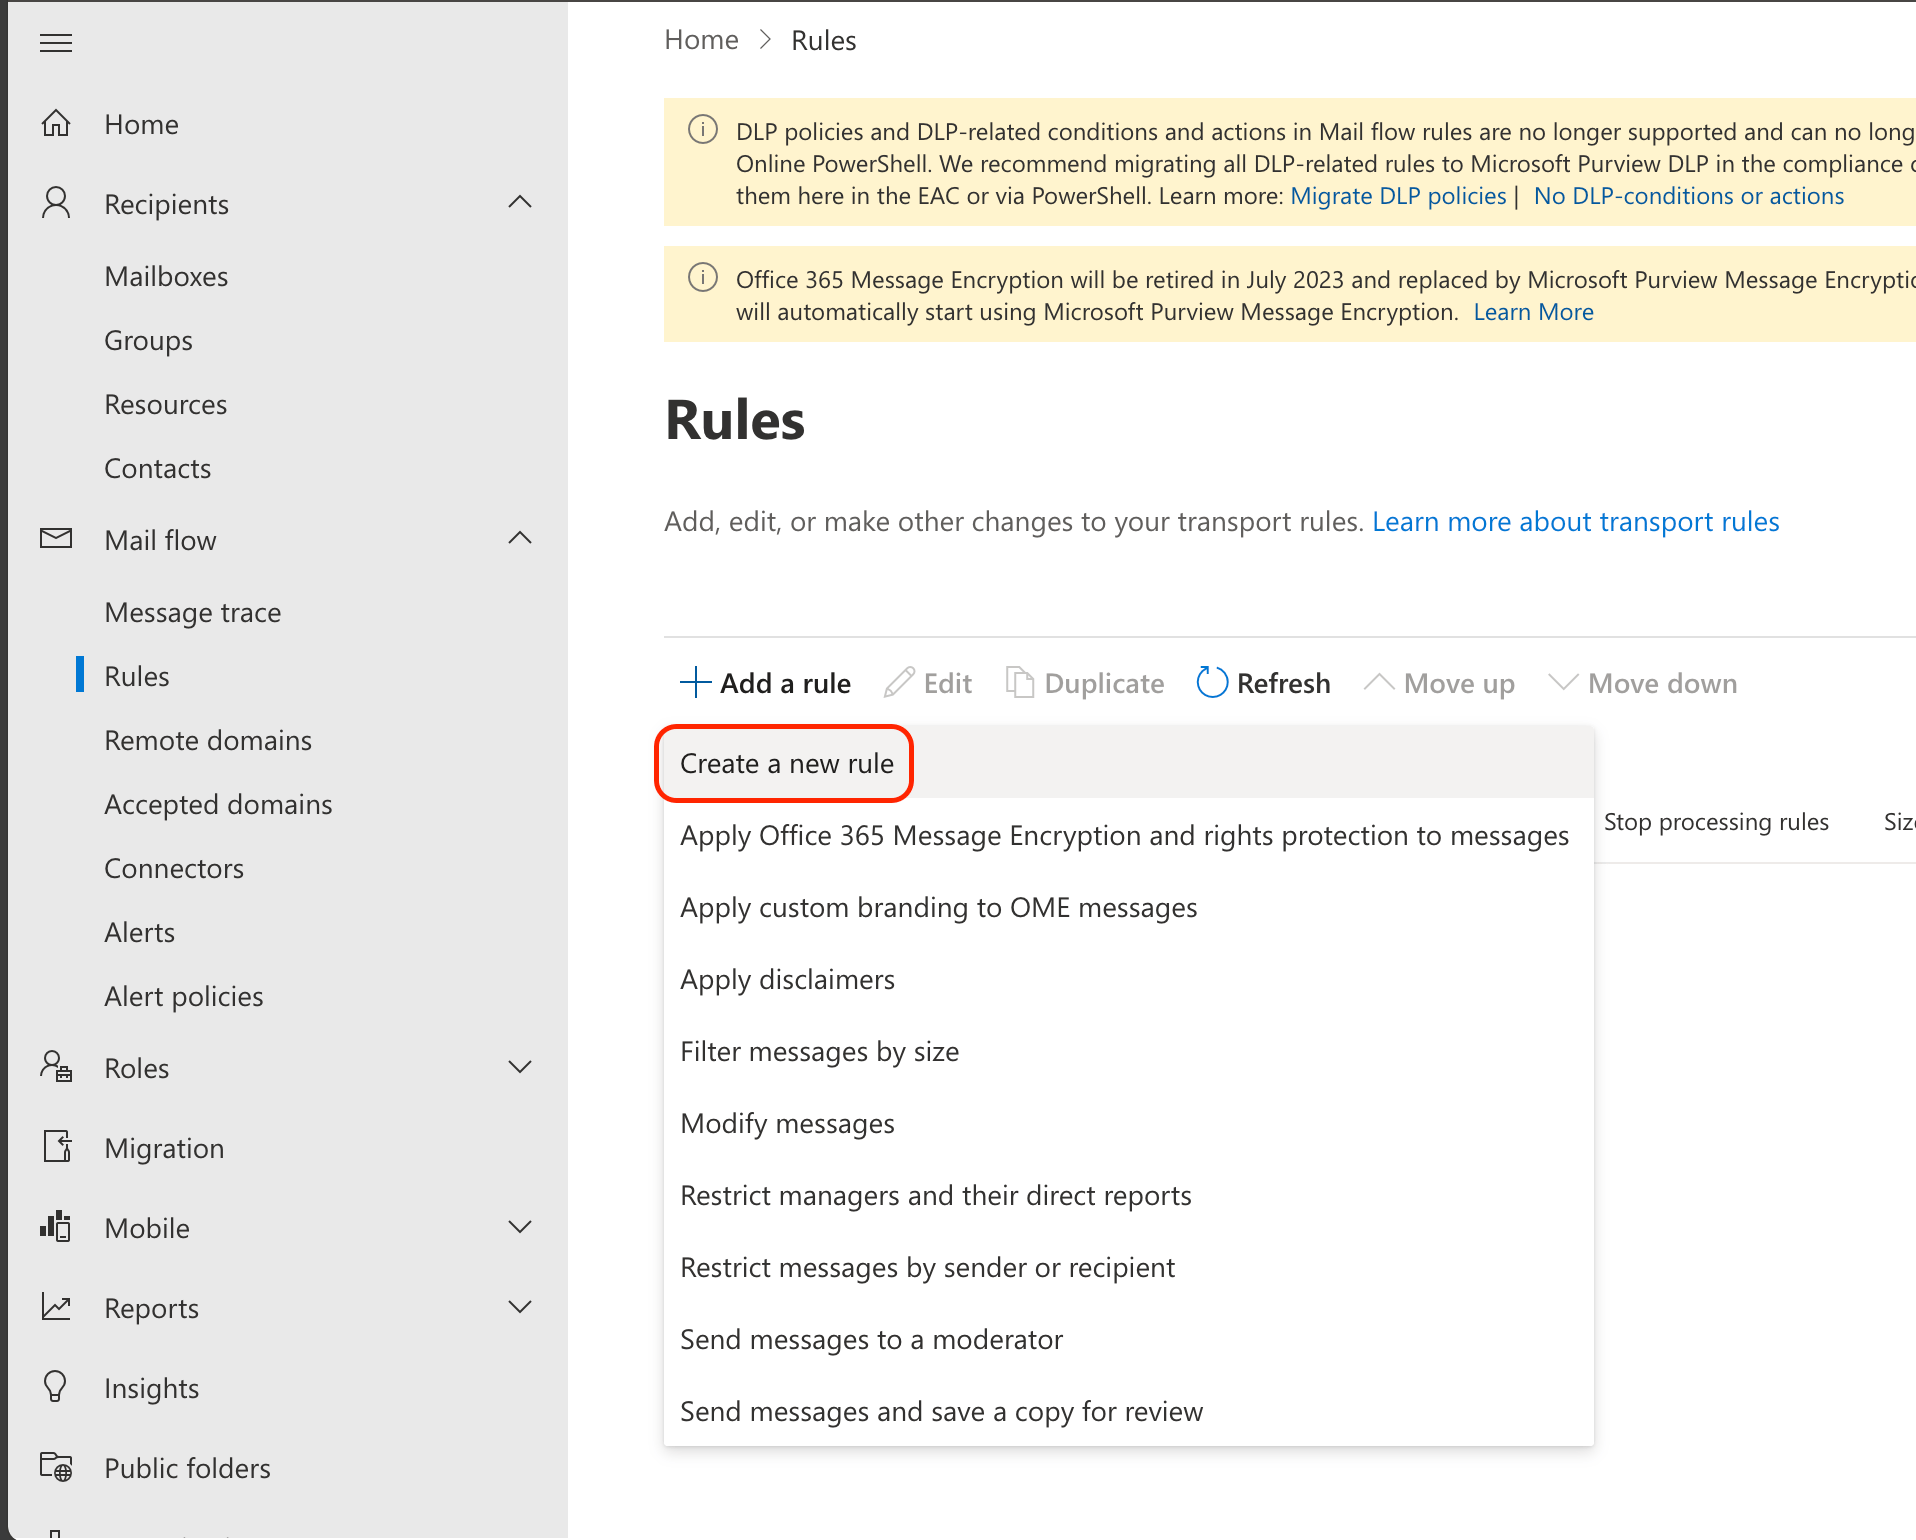
Go to Exchange Admin Center → Mail flow → Rules and create a new rule:
-
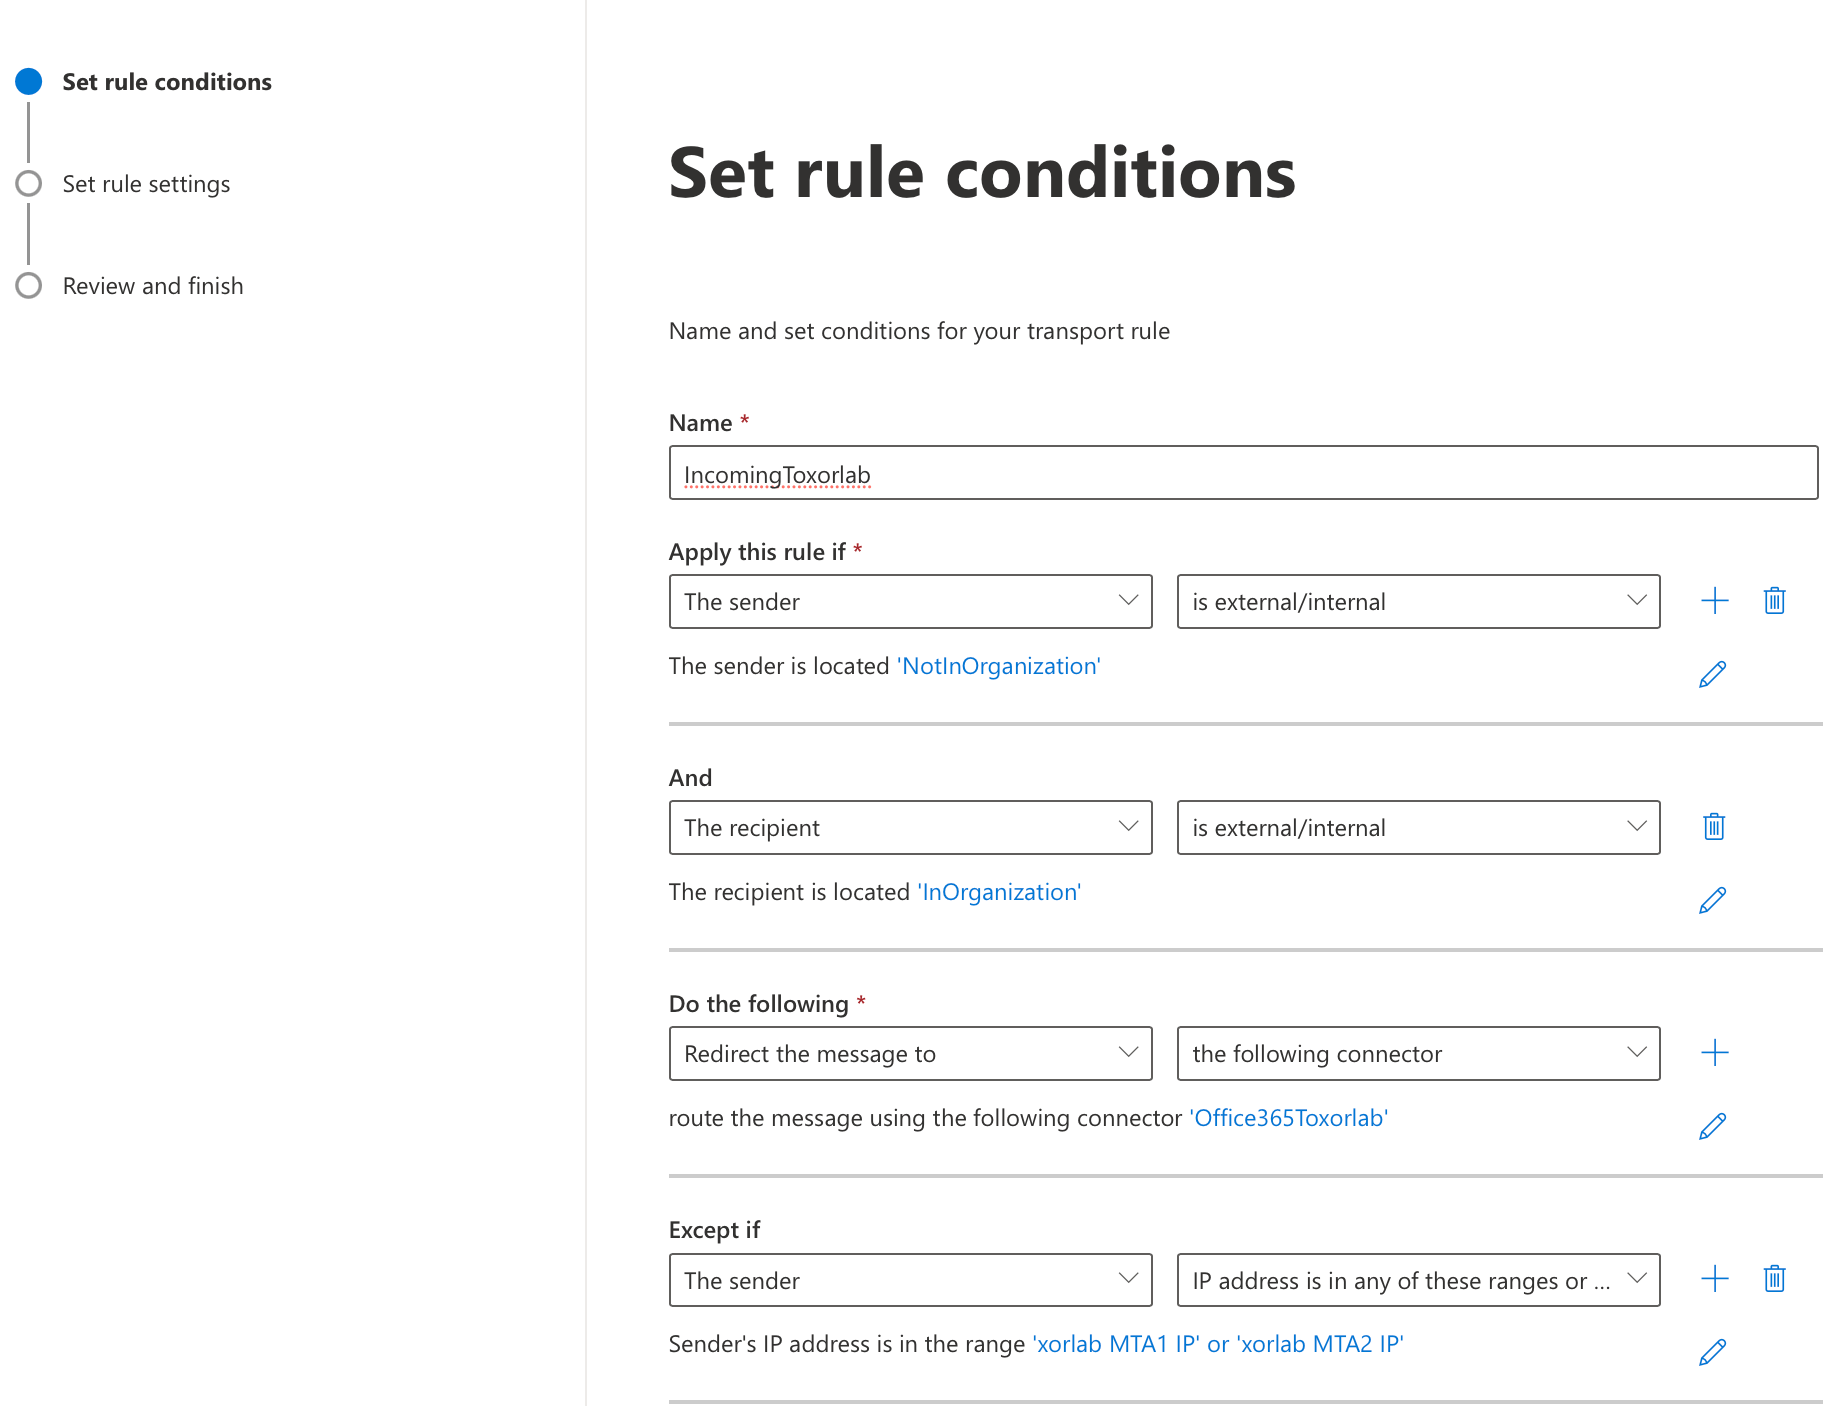
Configure the rule like this:
- Name:
IncomingToxorlab - Apply this rule if → The sender → is external/internal → Outside the organization
- Click the plus icon (
+) to add another condition - And → The recipient → is external/internal → Inside the organization
- Do the following → Redirect the message to → the following connector → choose Microsoft365Toxorlab
- Click the plus icon (
+) to add another action - And → Modify the message properties → set a message header → set
x-xor-tenant-tokento your header value - Except if → The sender → IP address is in any of these ranges… → add all IPs of the xorlab MTAs (find them in the DNS A records of
mx.xyz.activeguard.cloud)
- Name:
- Click through Next → Finish and leave all settings at their defaults.
-
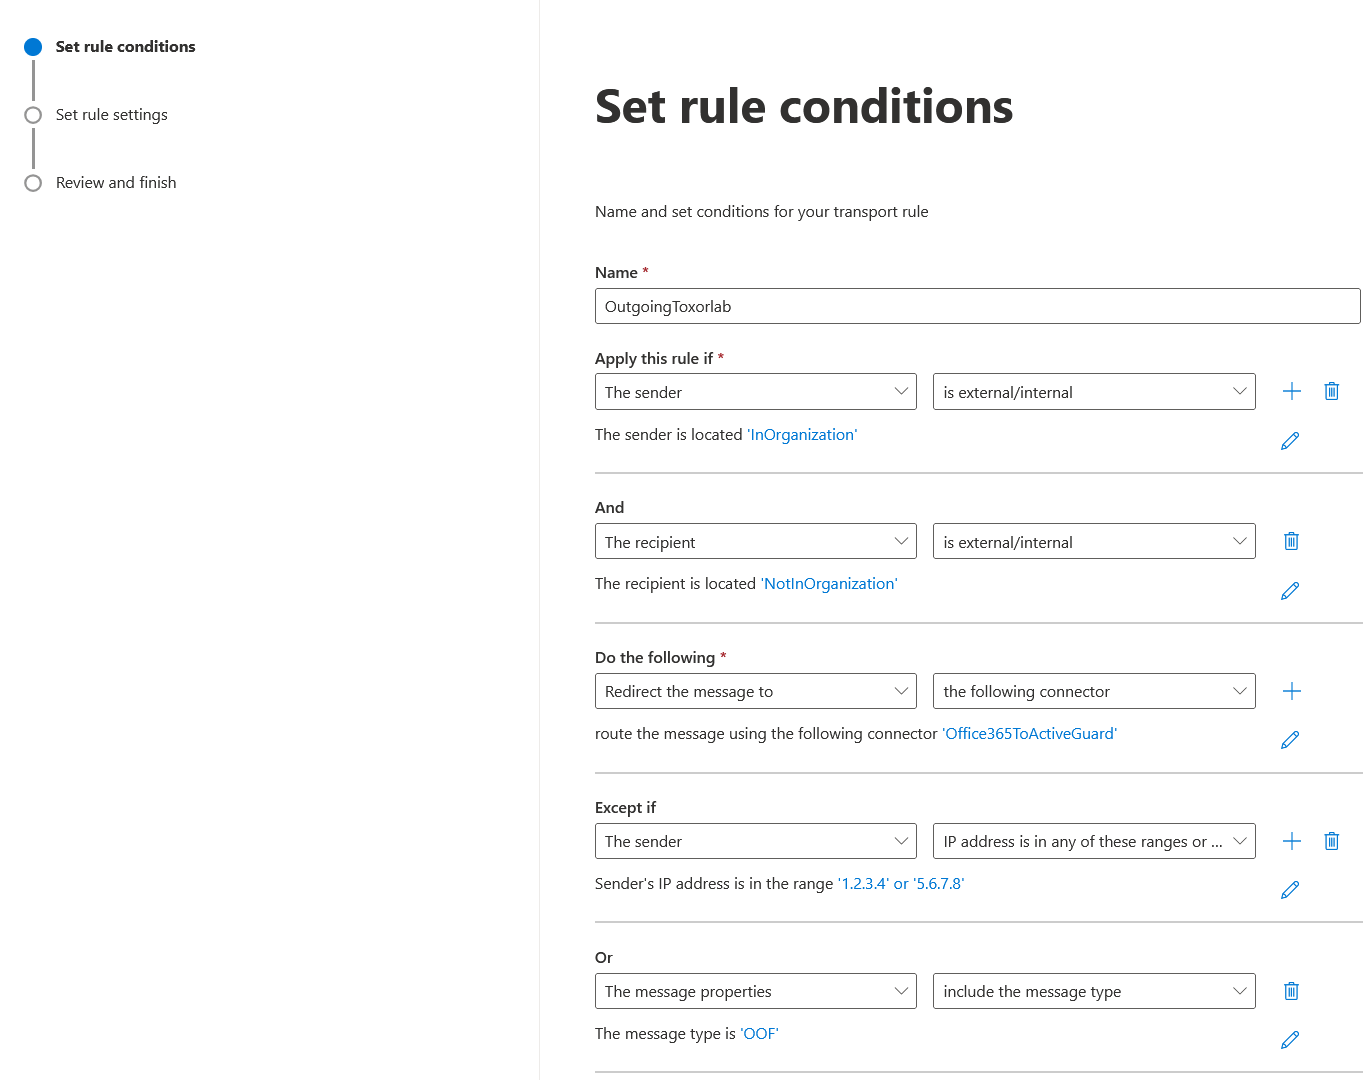
Repeat steps #2-3 to add another rule but this time set:
- Name:
OutgoingToxorlab - The sender → Inside the organization
- The recipient → Outside the organization
- Except if → The sender → IP address is in any of these ranges… → the same xorlab MTA IPs as in step #2
- Click the plus icon (
+) to add another exception - The message properties → Automatic Reply
- Name:
- Enable both rules in the Rules page.
- It can take several minutes until the rule is active. Test it by sending an incoming and outgoing email.
Troubleshooting
Apply the following measures only if you experience deliverability issues between M365 and xorlab. Normally, they are not necessary.M365 rejects emails from xorlab
If M365 rejects some legitimate emails from xorlab, there are multiple measures. Apply them in order written below until the problem is fixed. First, add your xorlab domain as an “accepted domain”.Add xorlab as accepted domain
Add xorlab as accepted domain
-
Go to Microsoft 365 Admin Center → Settings → Domains and add a domain:
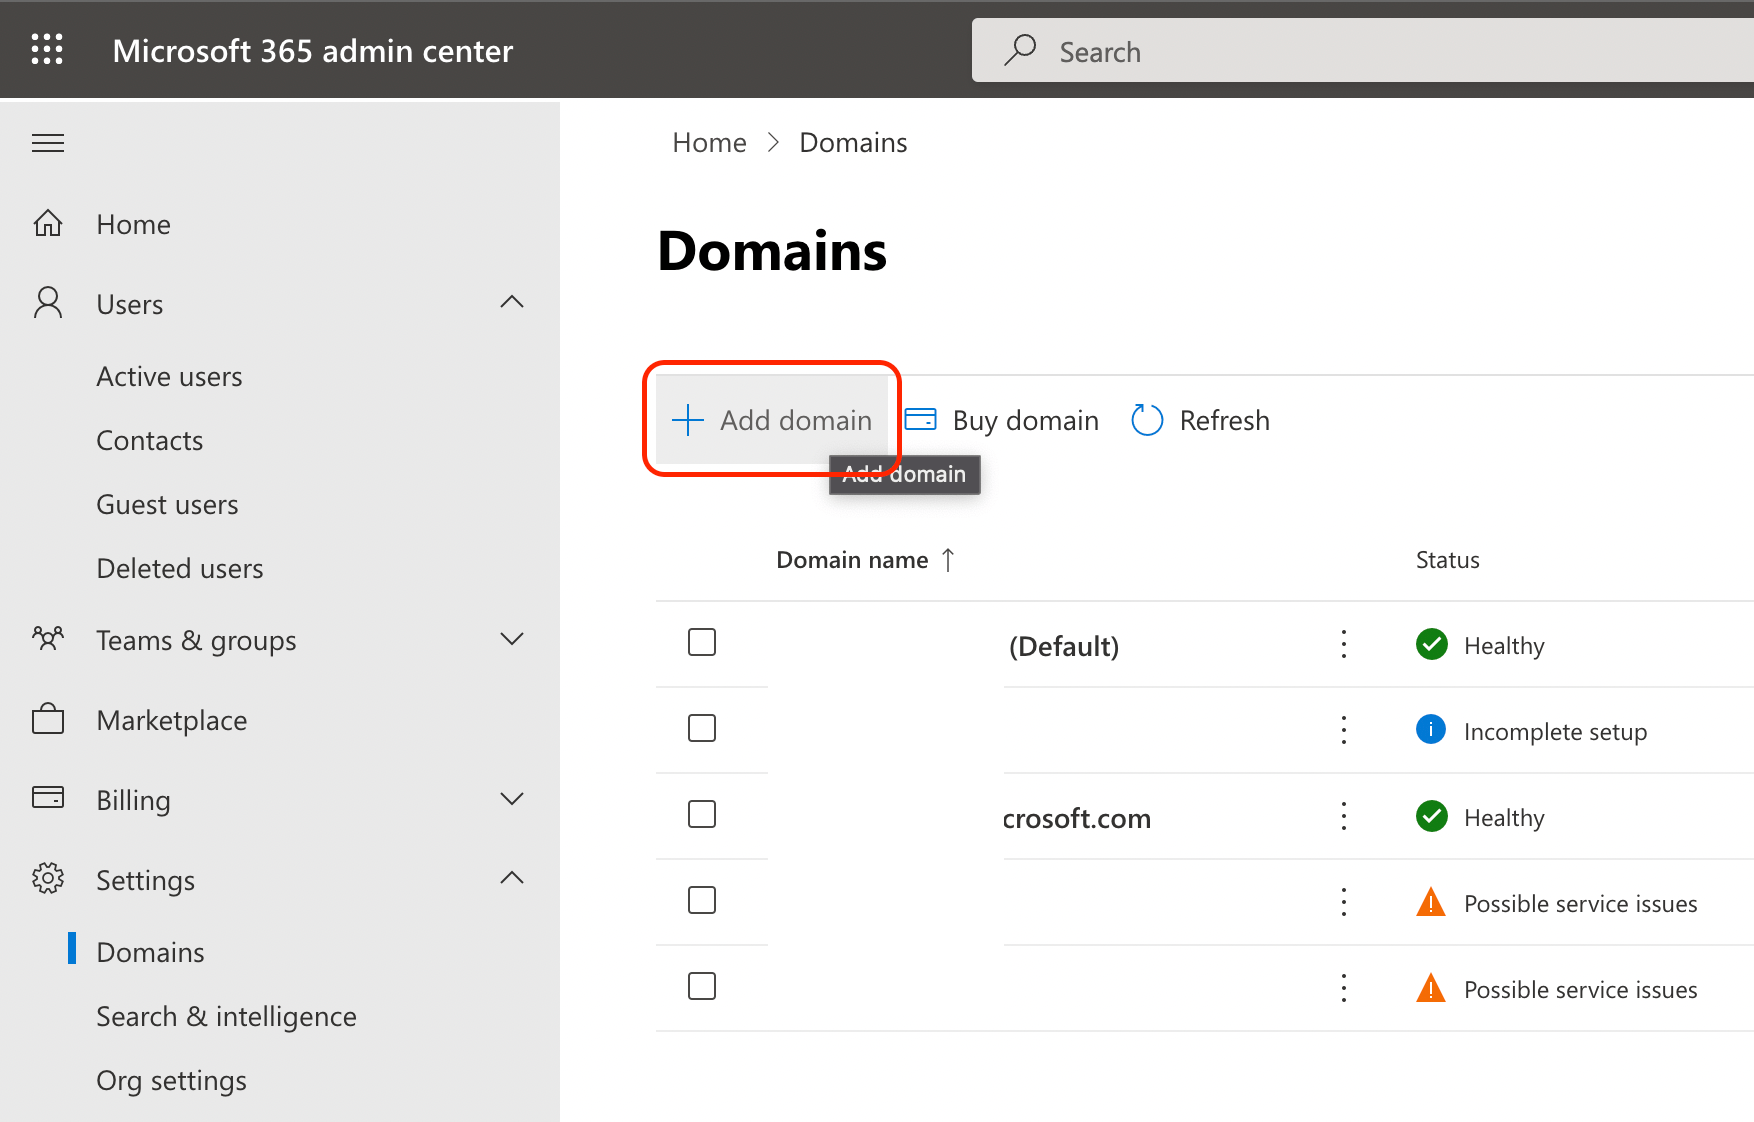
-
Enter
xyz.activeguard.cloud, wherexyzis your customer ID: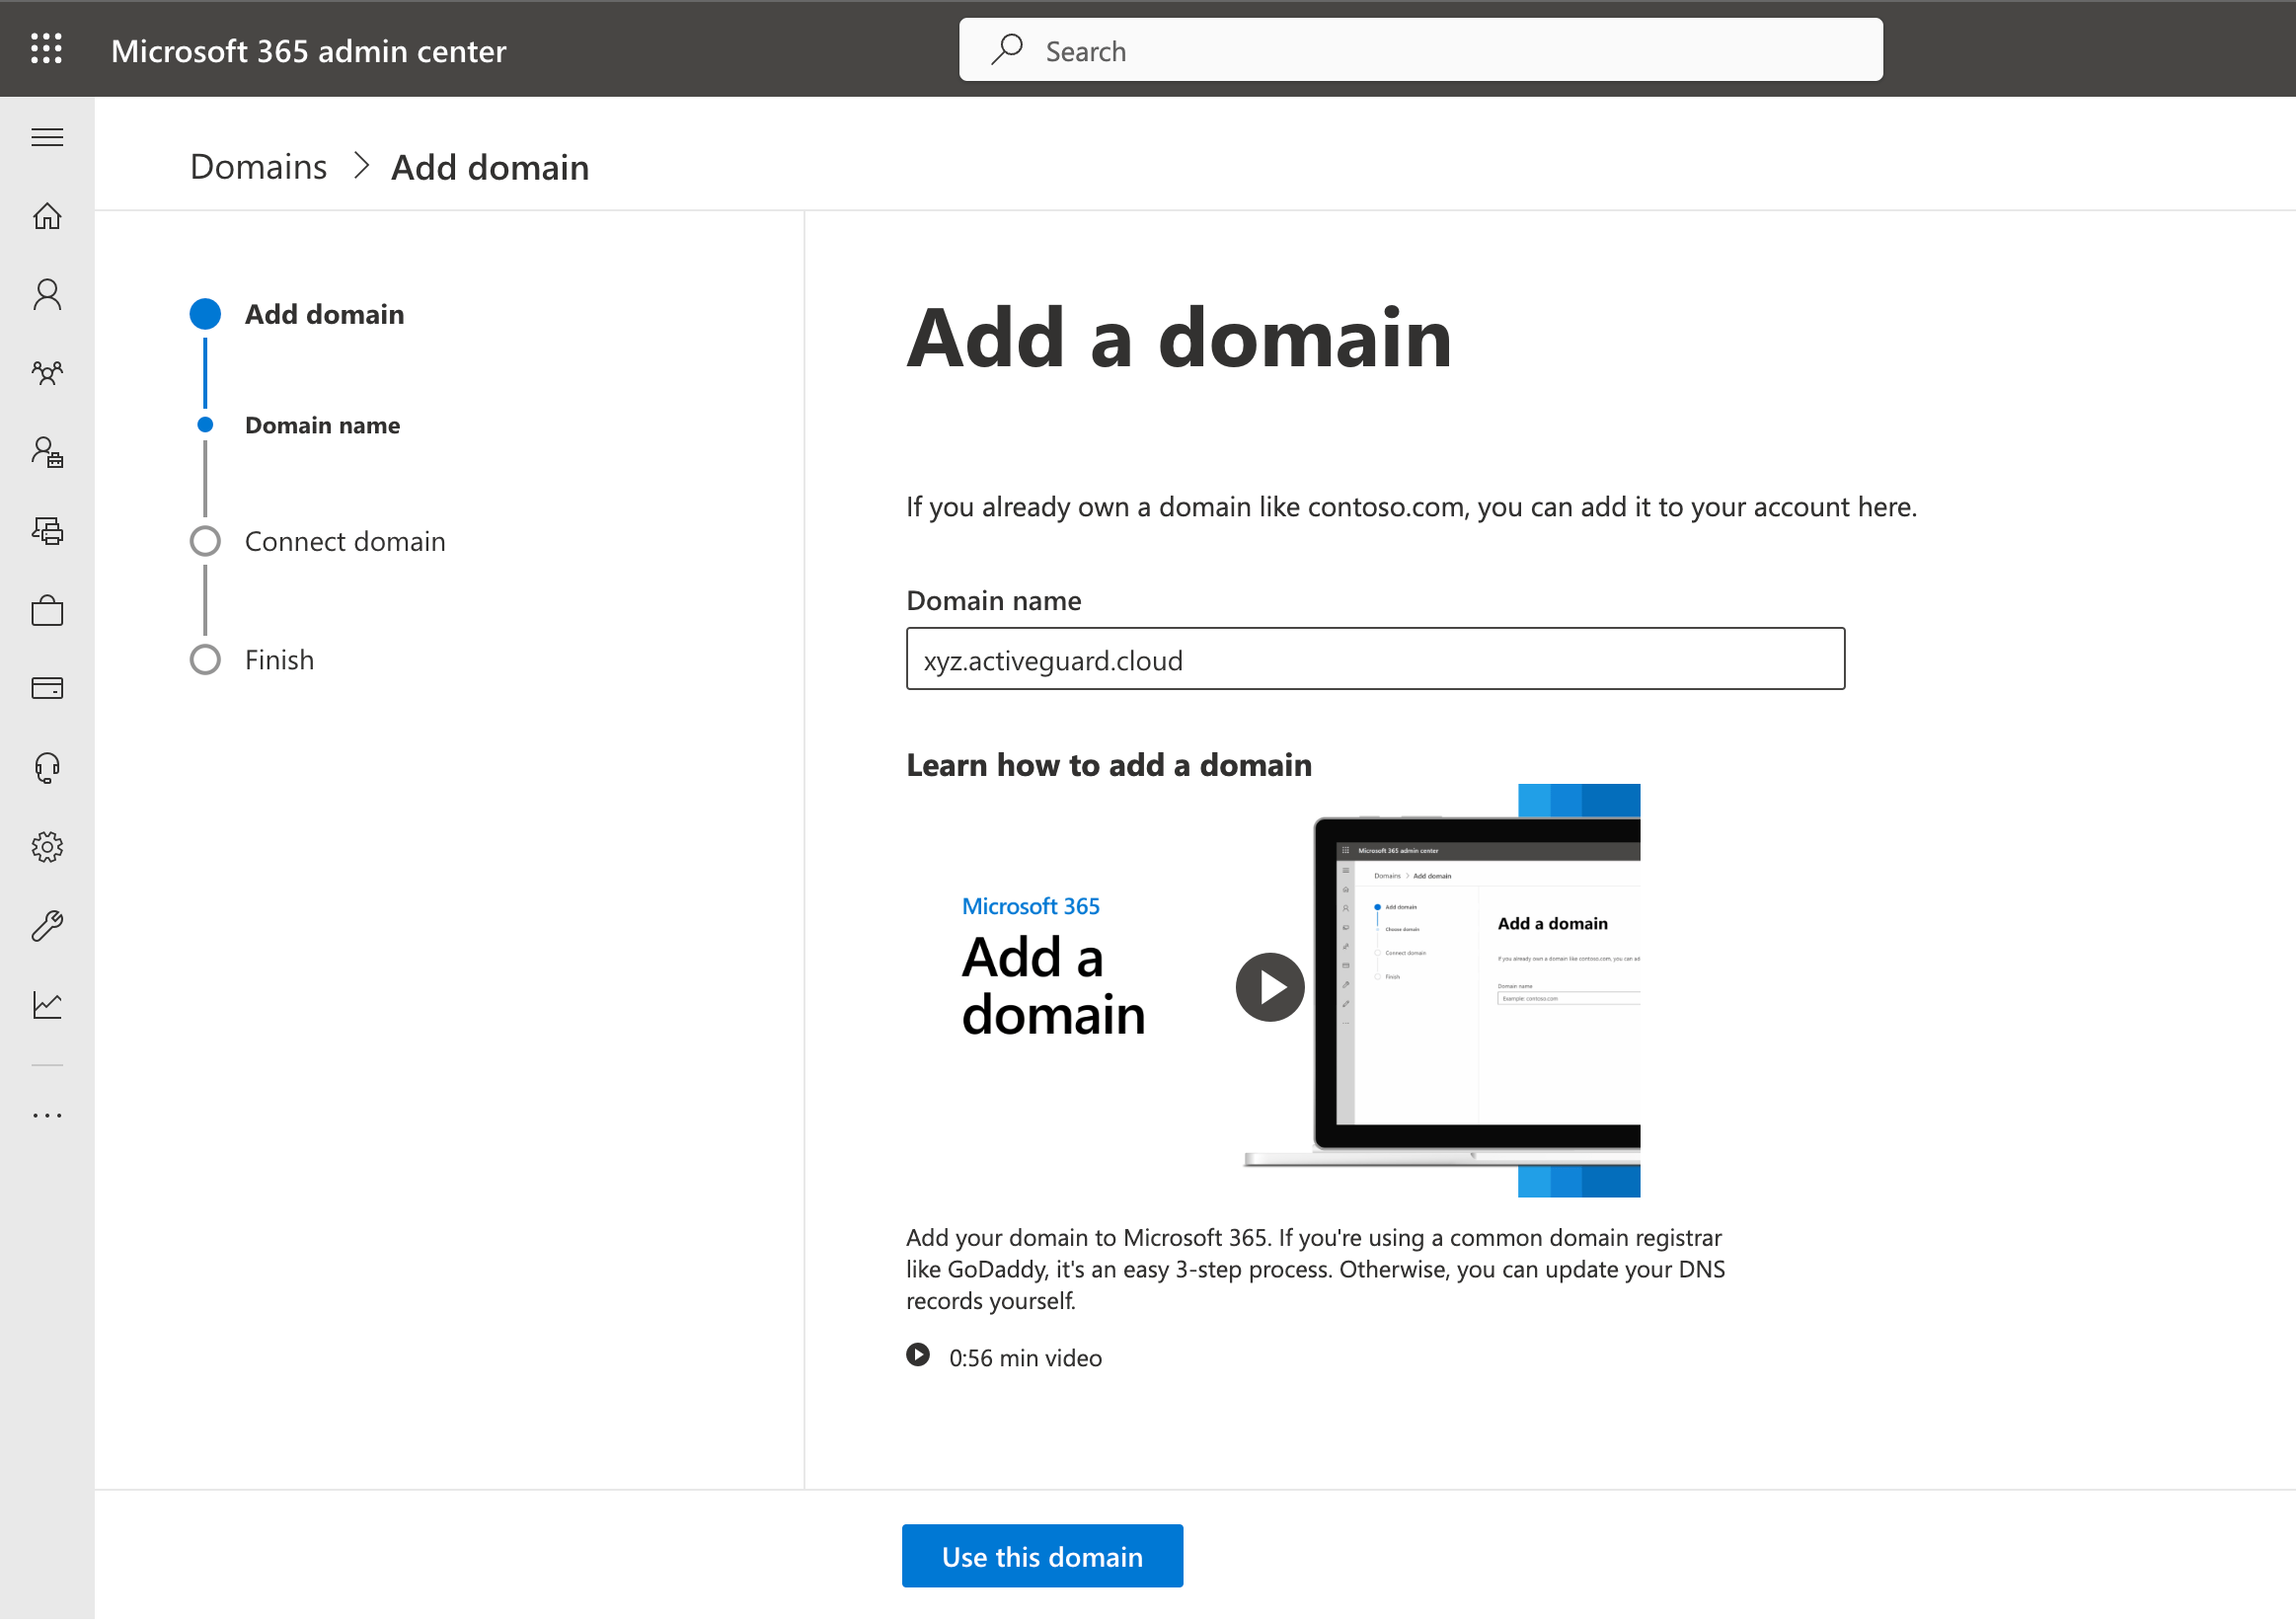
-
Select the first option Add a text record…:
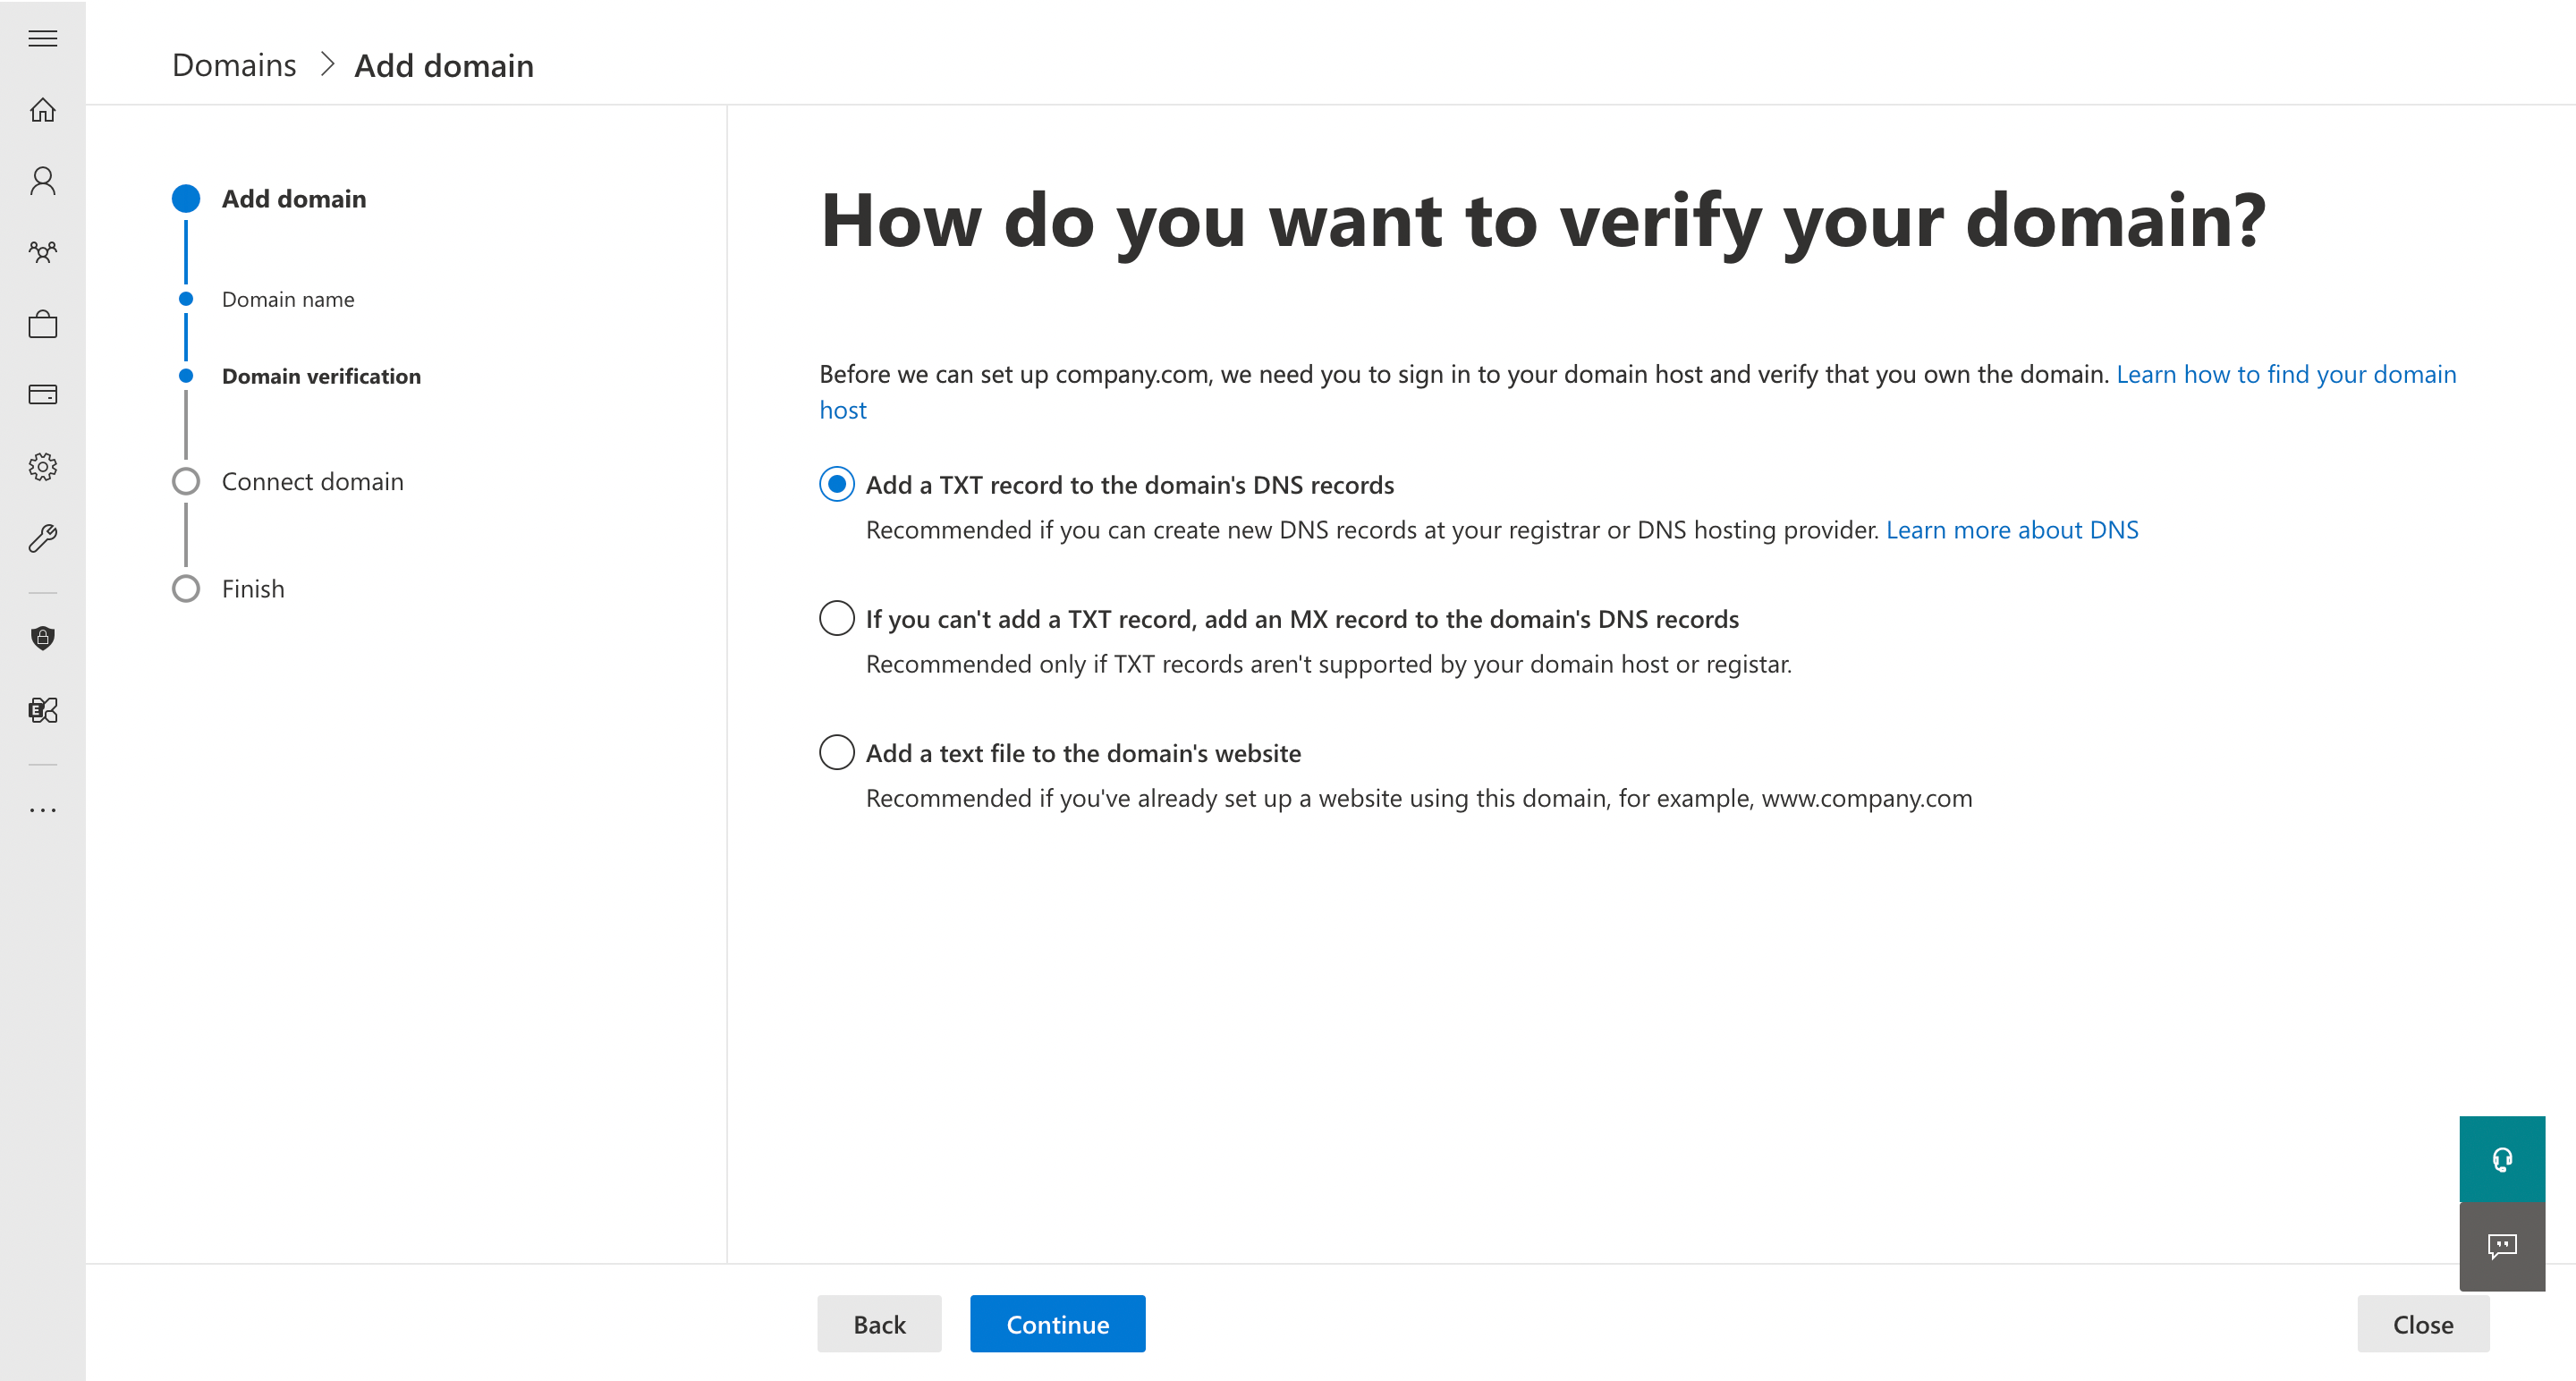
-
Send the TXT value to support@xorlab.com so that we can add it to the DNS record of your domain. After this has been done, verify:
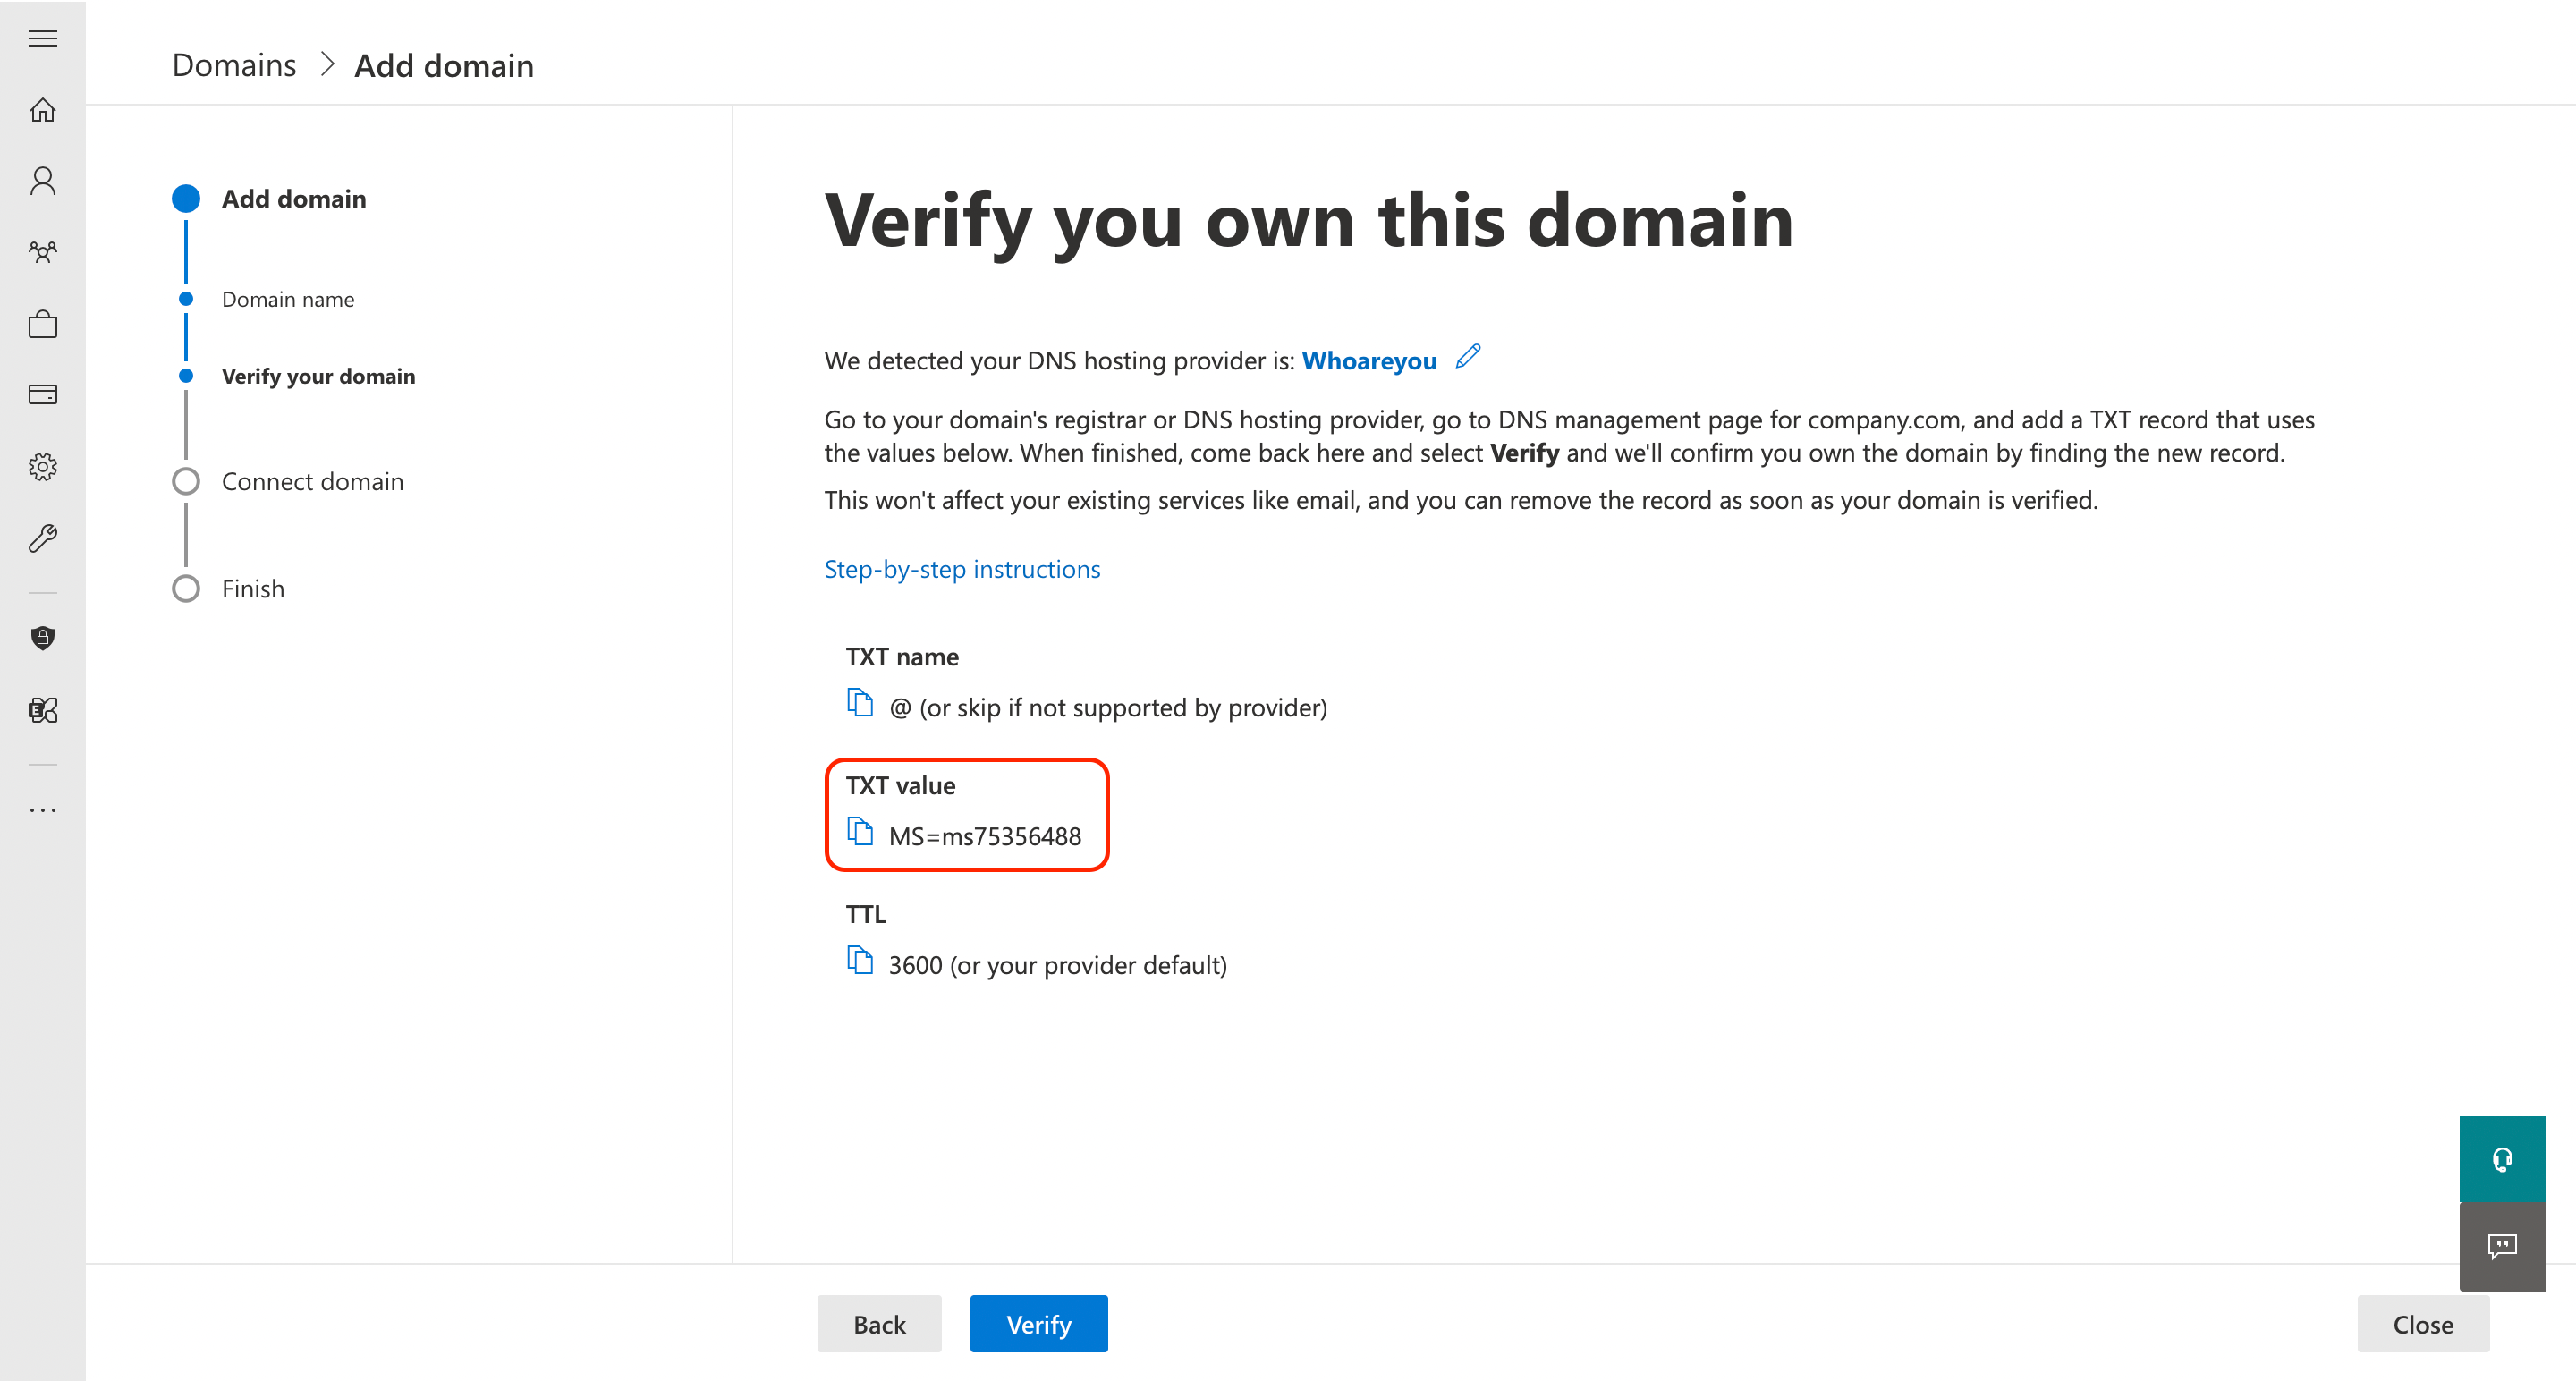
-
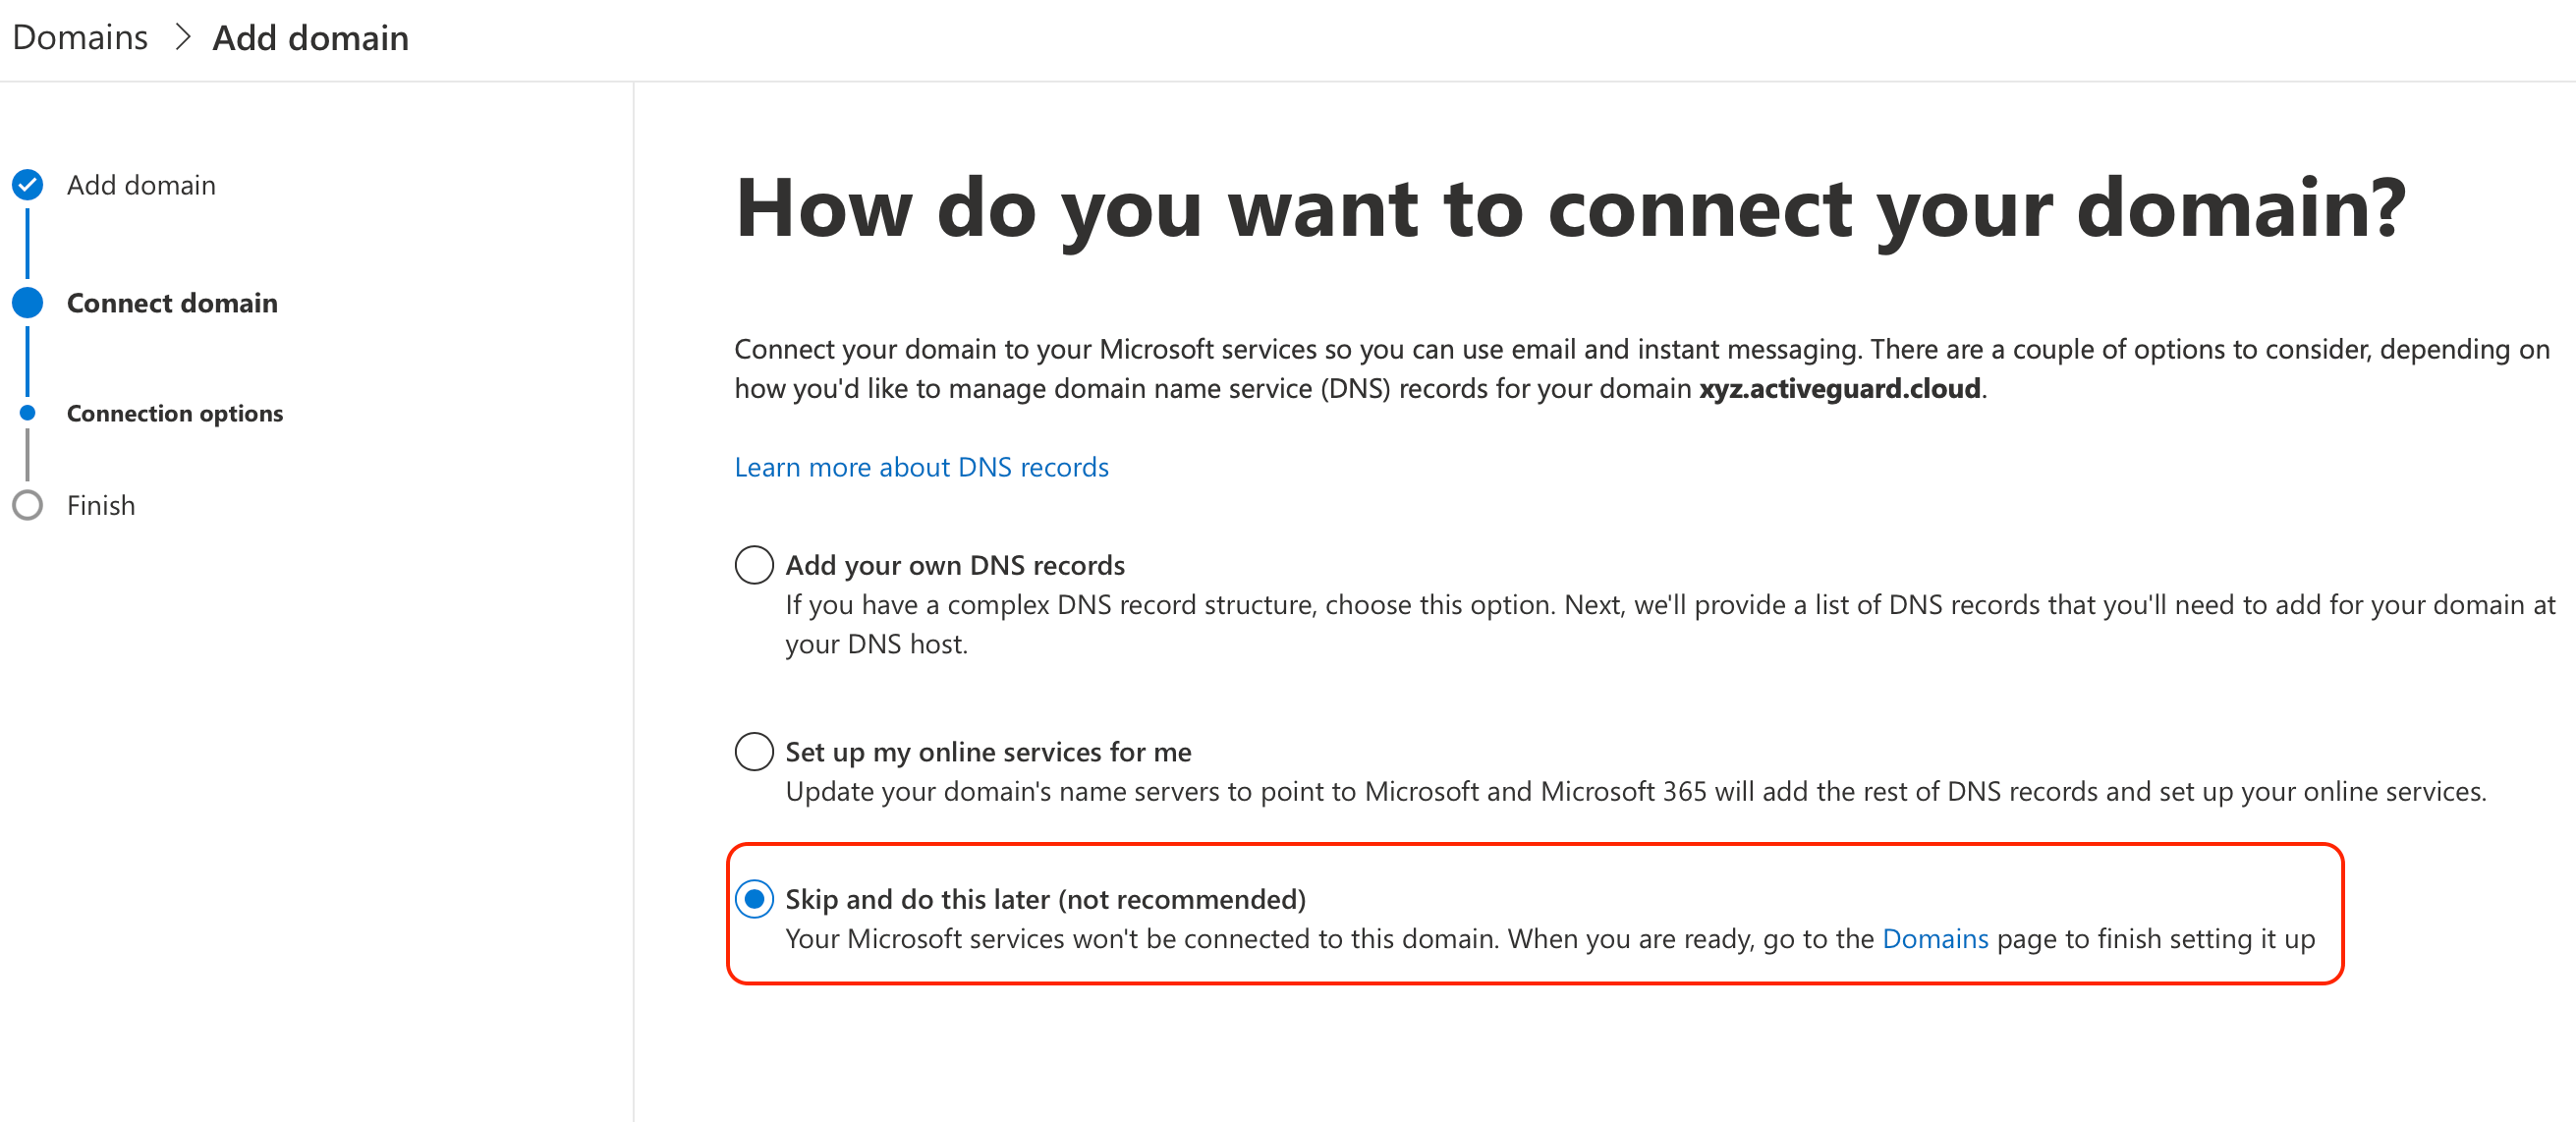
After a successful verification, click More options and select Skip and do this later:
Add xorlab to your SPF records
Add xorlab to your SPF records
You can add the xorlab MTAs to your SPF records. For this, include Afterward, check that your SPF records are still valid, for example with DMARCanalyzer’s SPF checker.
a:mx.xyz.activeguard.cloud to all your domains that route emails via xorlab:Add xorlab to the M365 anti-spam policy
Add xorlab to the M365 anti-spam policy
-
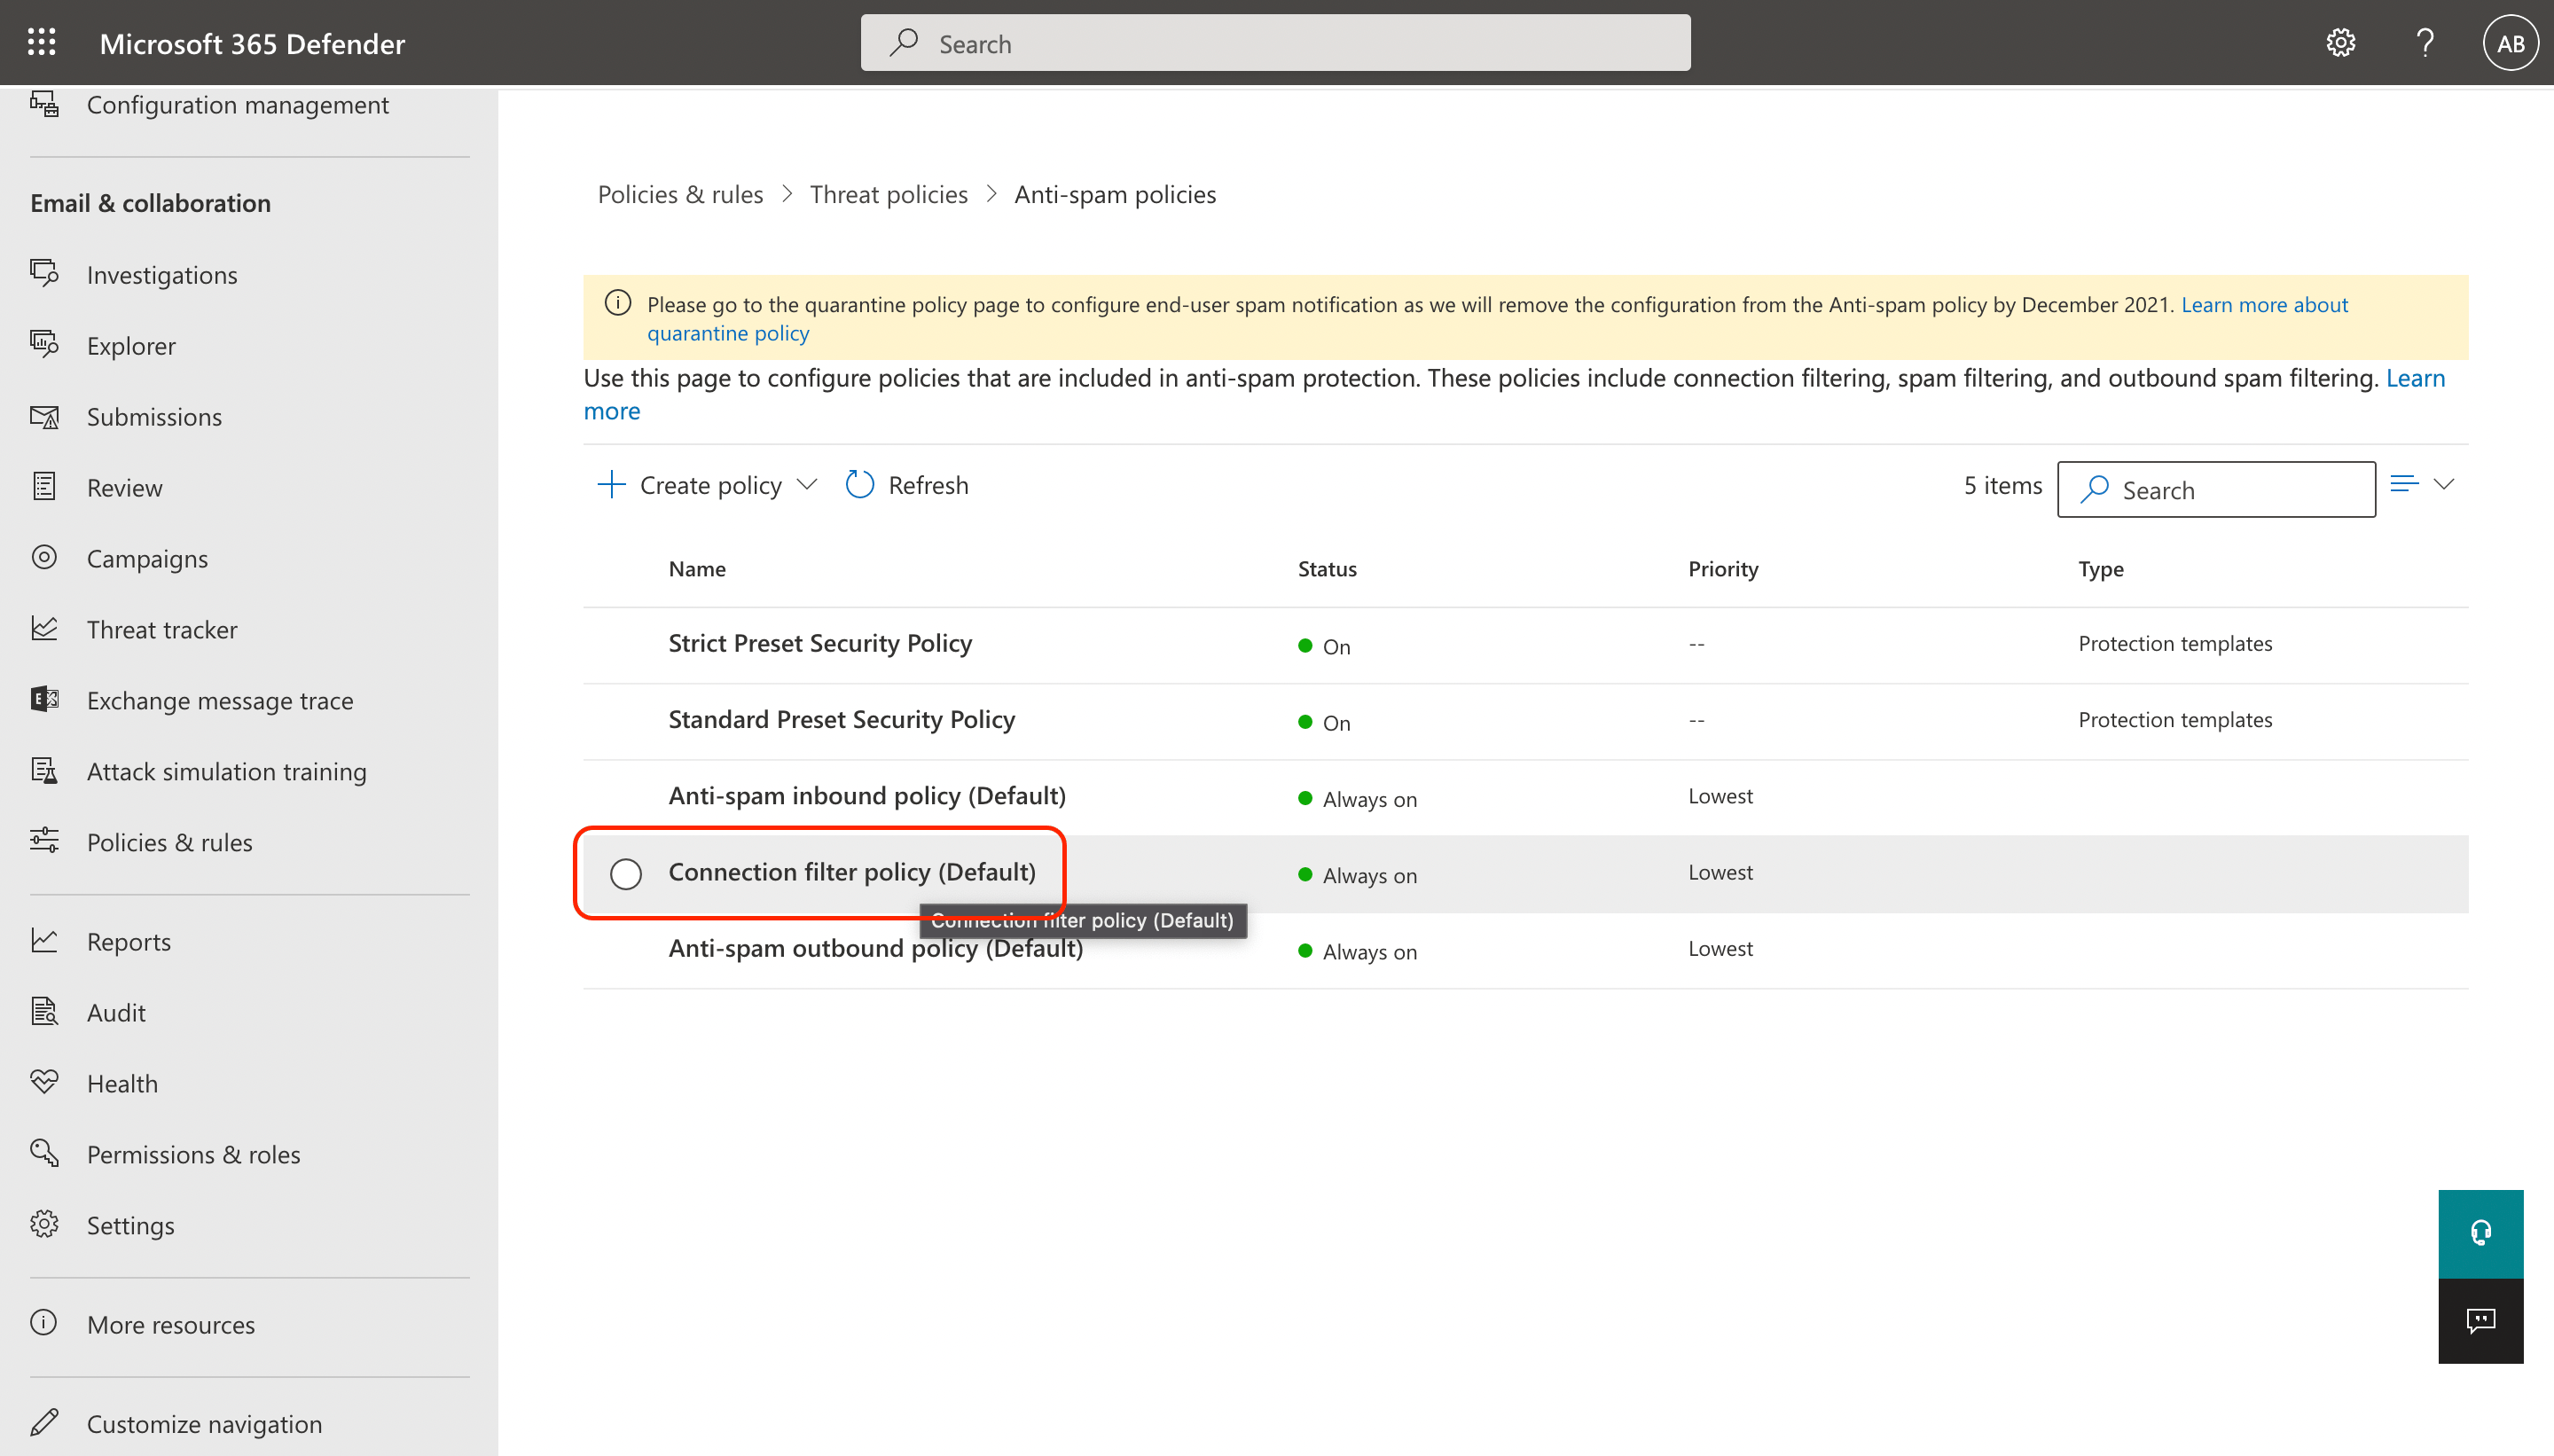
Go to Anti-spam policies and select Connection filter policy (Default):
-
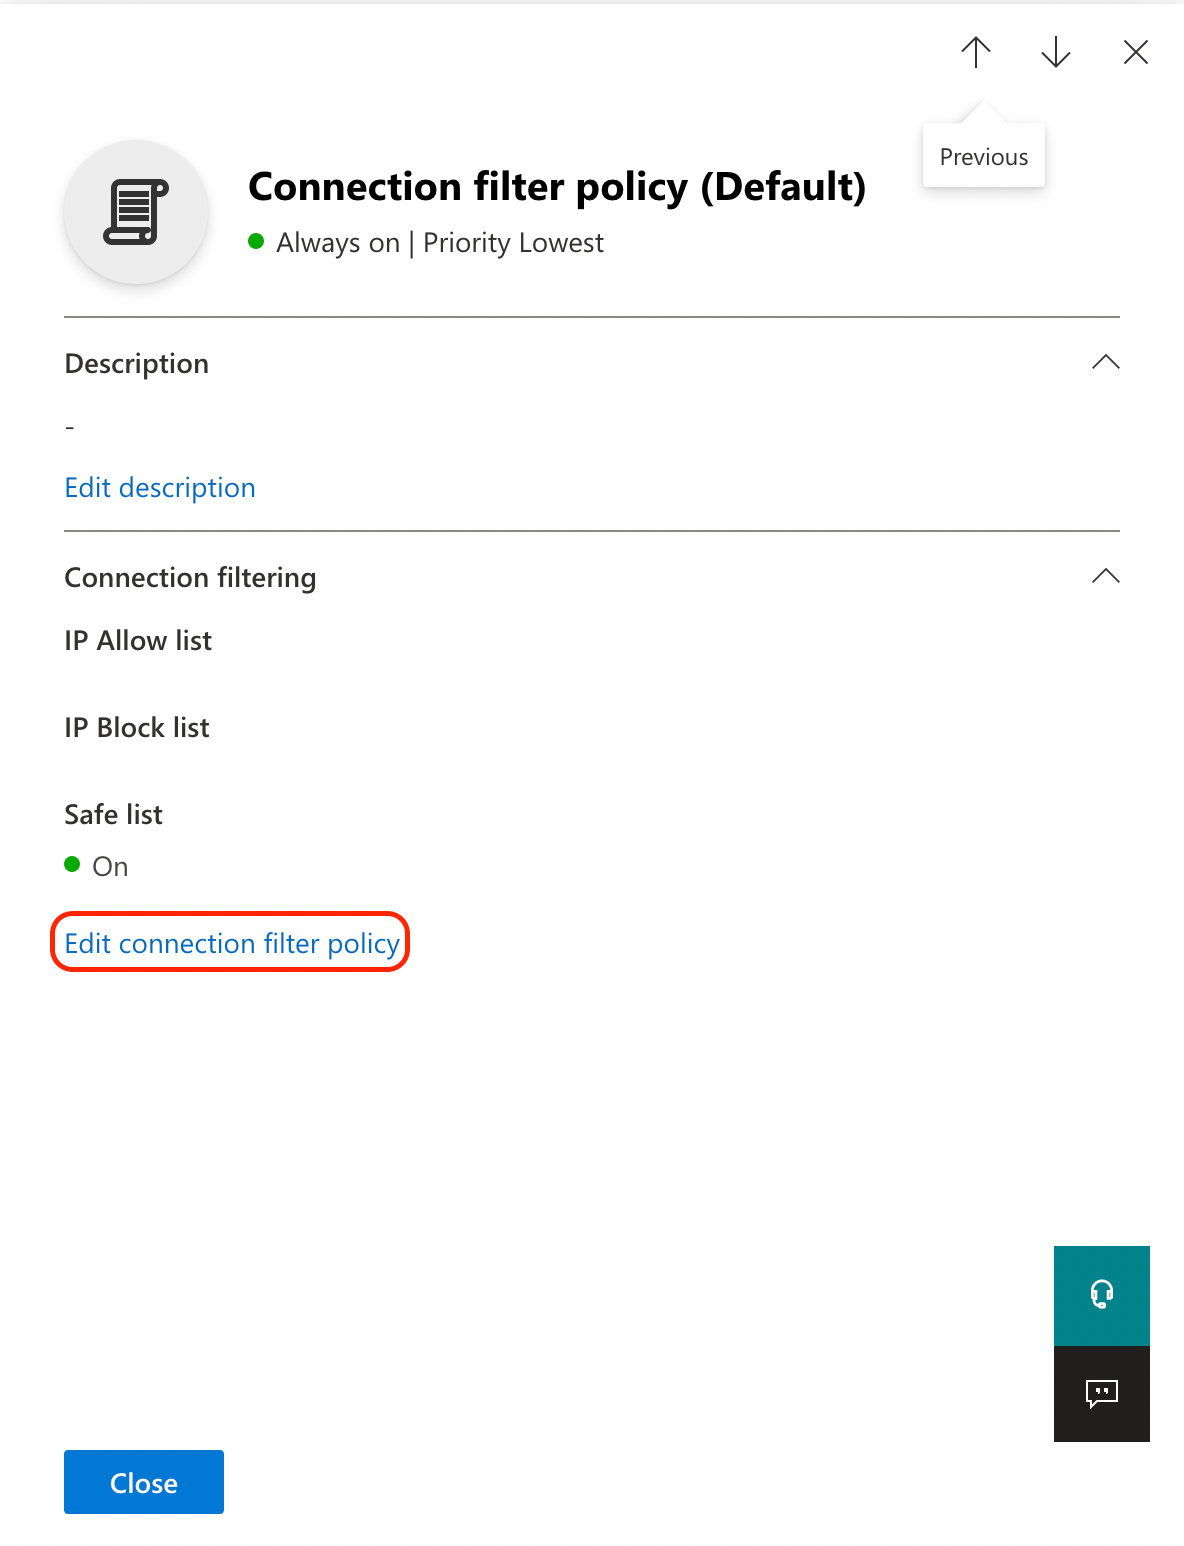
Click Edit connection filter policy:
-
Enter the xorlab MTA IPs to the first field:
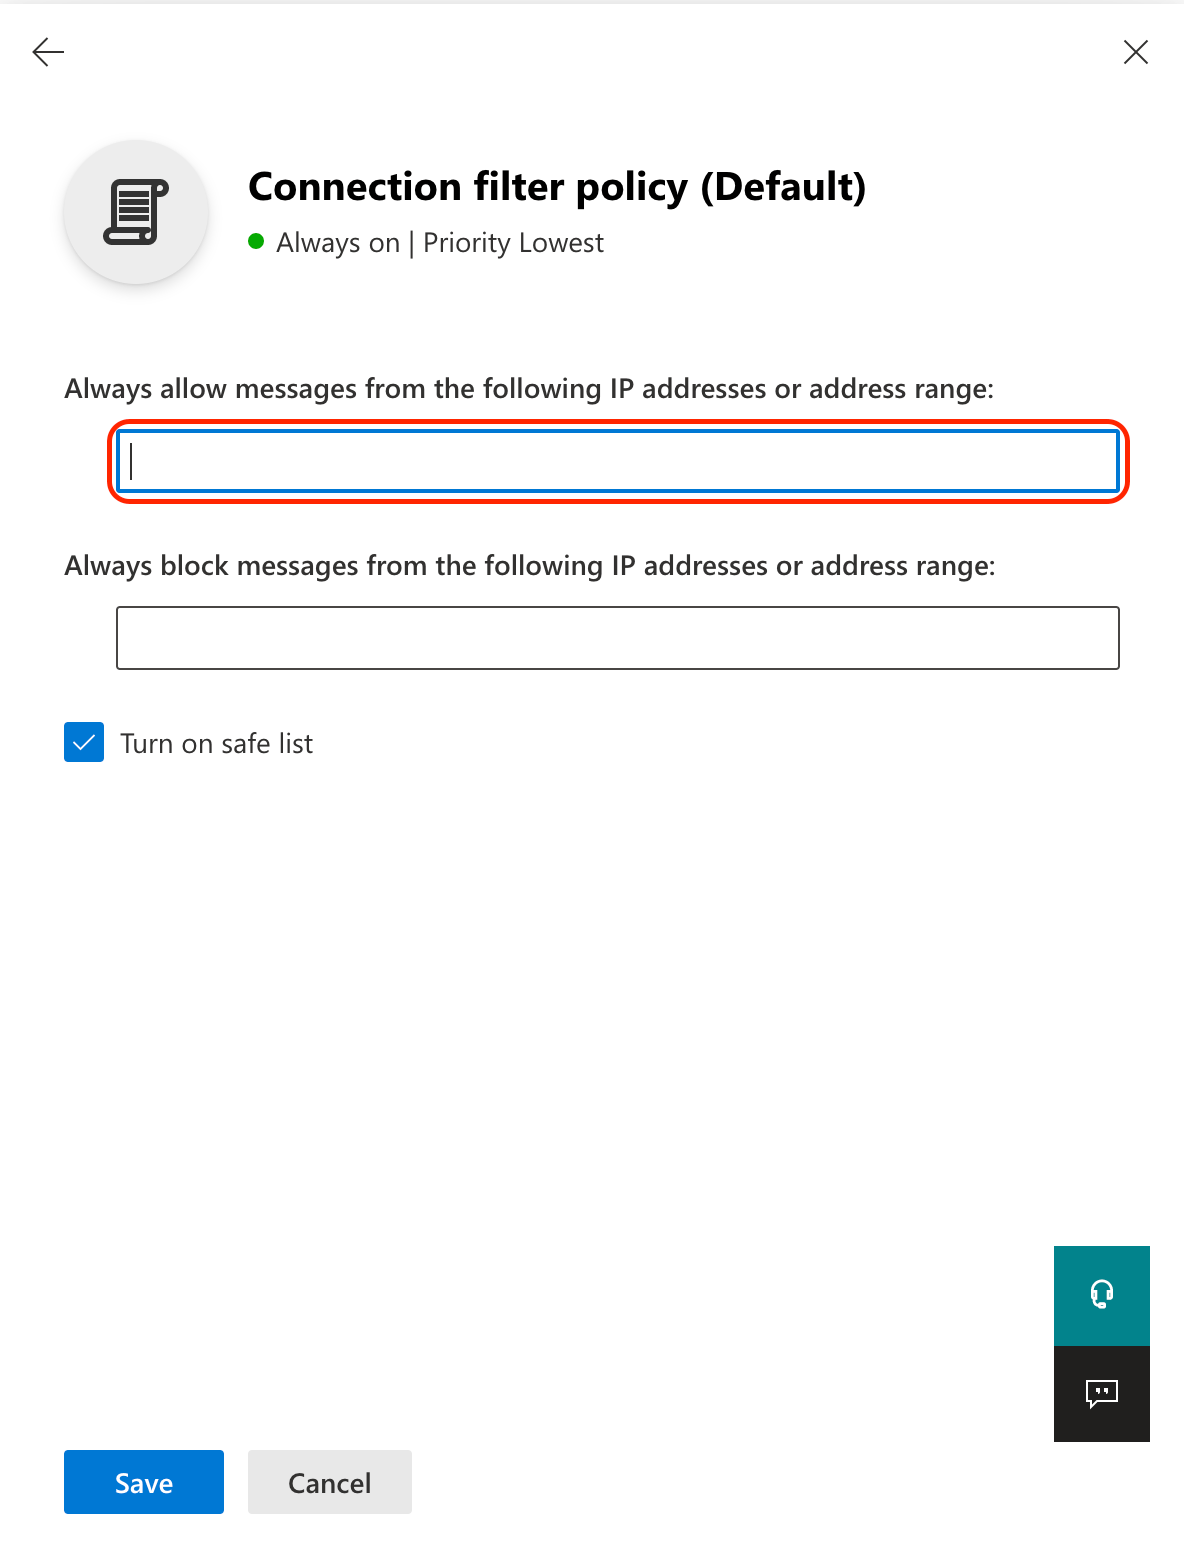
- Check if the addresses are correct under IP Allow list and click Close.
M365 puts emails from xorlab into Junk
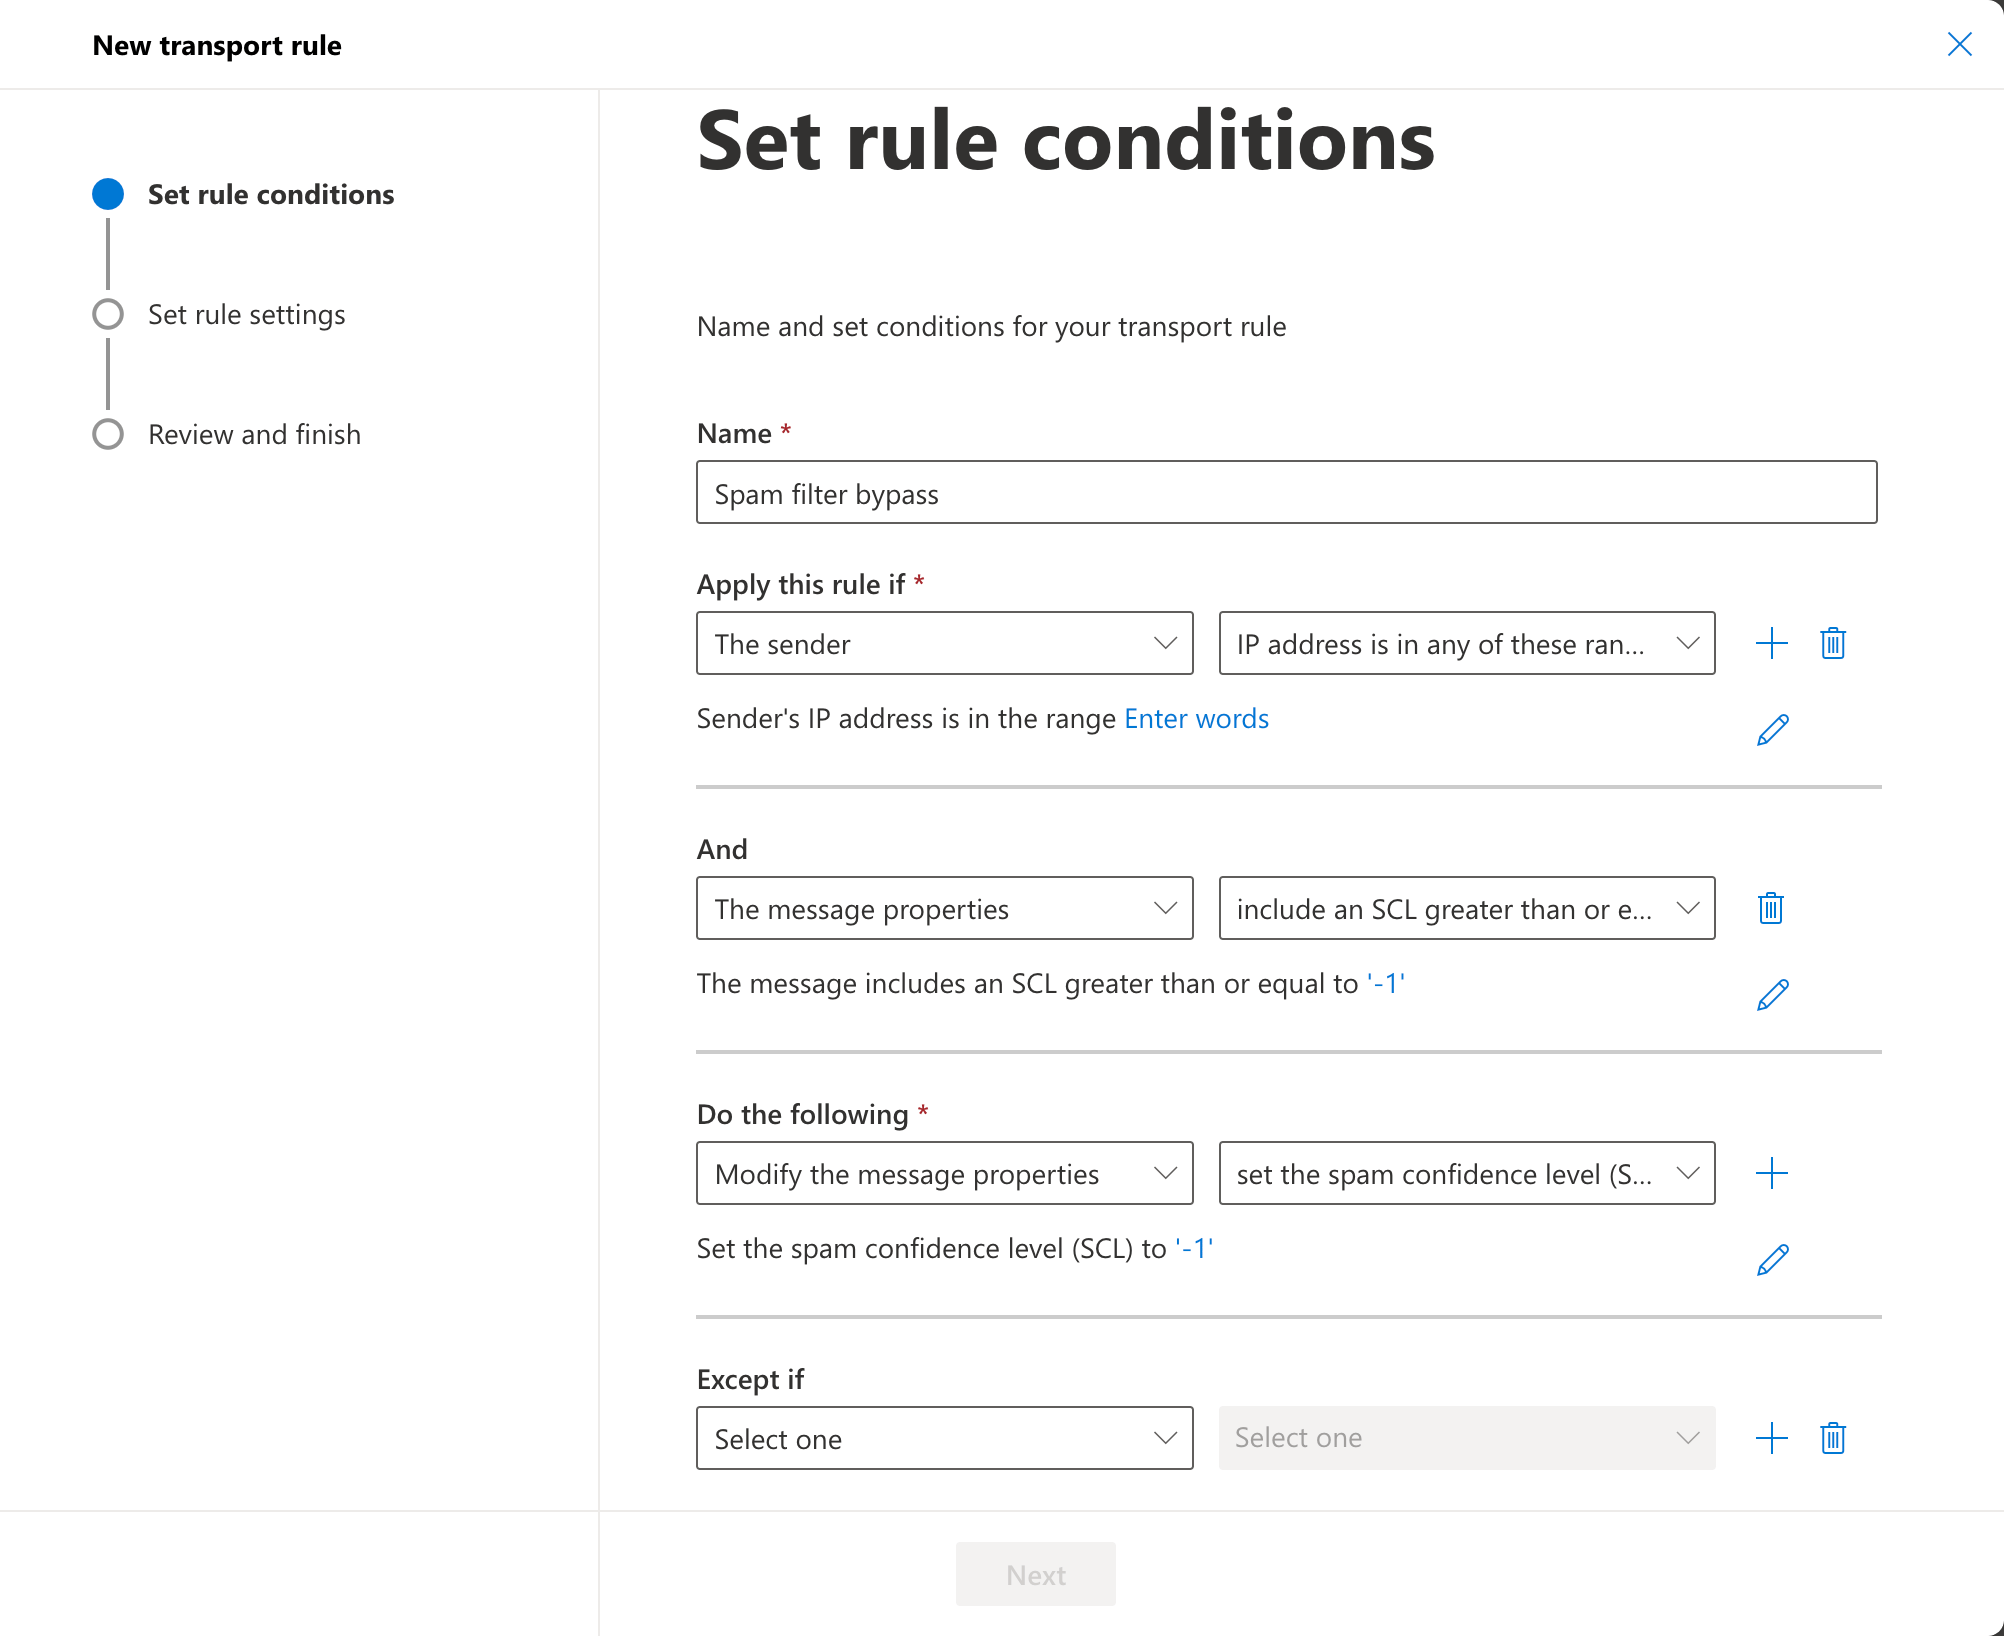
The following mail flow rule will bypass the M365 spam filtering for emails coming from xorlab. Note that this will mostly disable the Junk folder mechanism for your mailboxes.Bypass spam filtering
Bypass spam filtering
-
Go to Exchange Admin Center → Mail flow → Rules and create a new rule:
-
Configure the rule like this:
-
Name:
SpamBypassxorlab. - Apply this rule if → The sender → IP address is in any of these ranges… → add all IPs of the xorlab MTAs
-
Click the plus icon (
+) to add another condition - And → The message properties → include an SCL greater than or equal to → Bypass spam filtering
-
Do the following → Modify the message properties → set the spam confidence level (SCL) → Bypass spam filtering
-
Name:
- Click through Next → Finish and leave all settings at their defaults.
- Enable the rule in the Rules page.